Or Weis
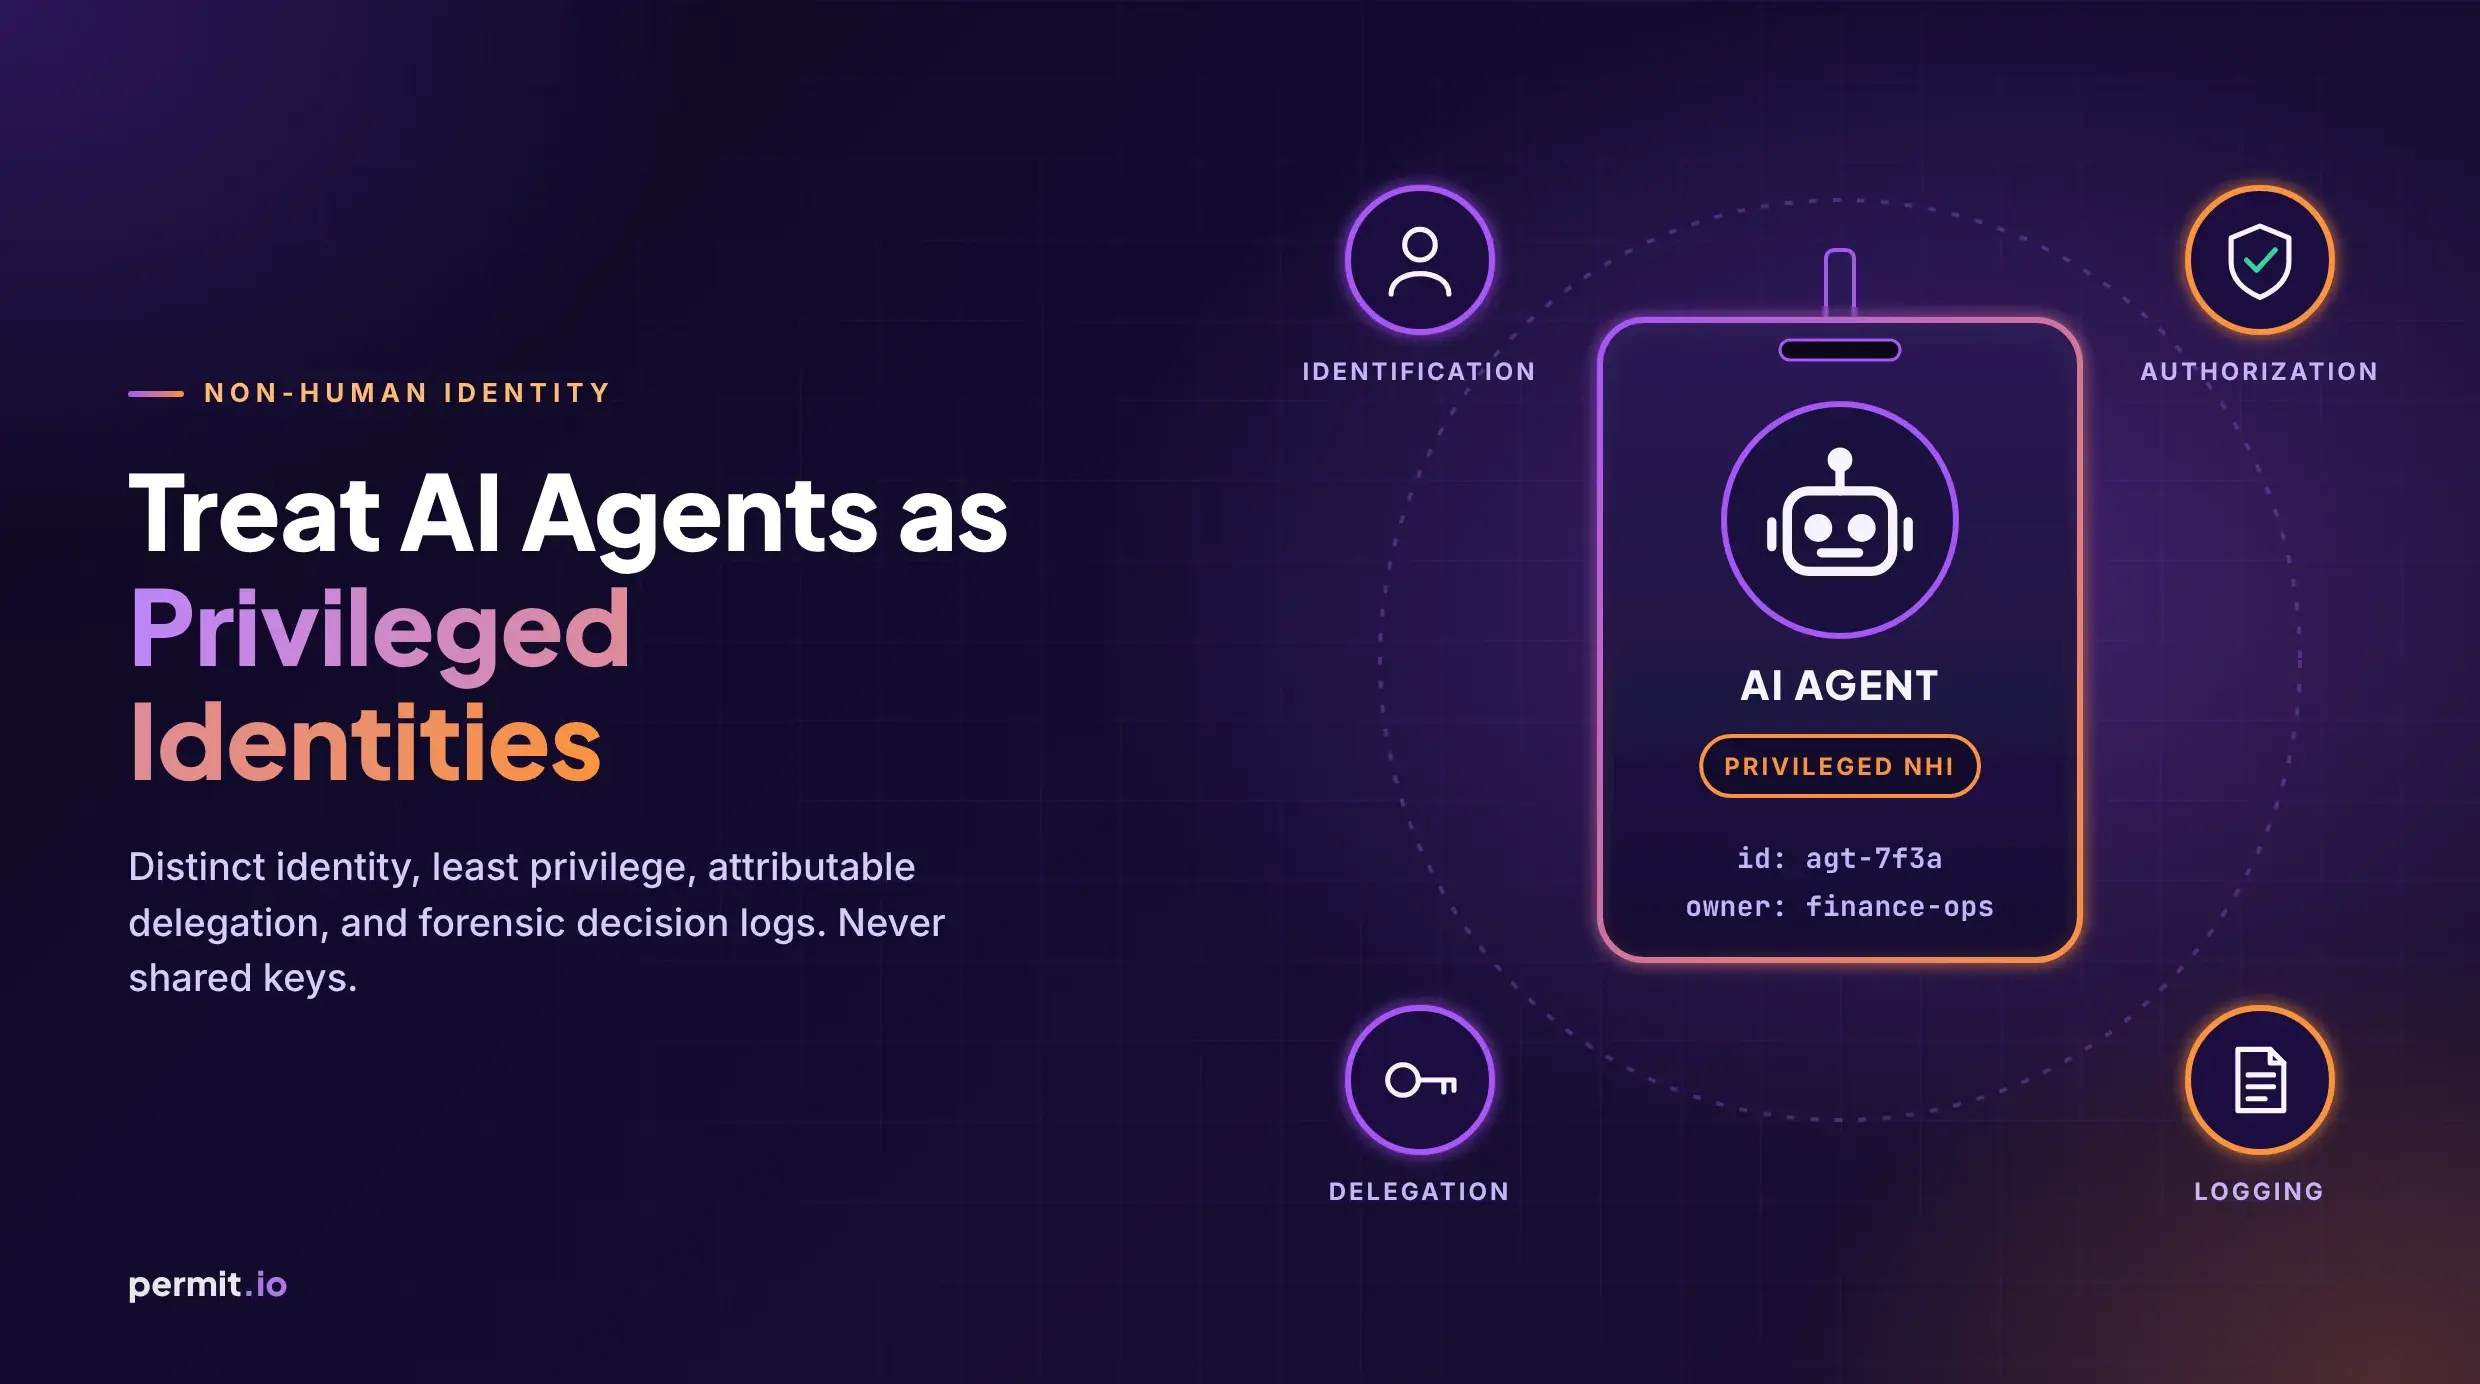
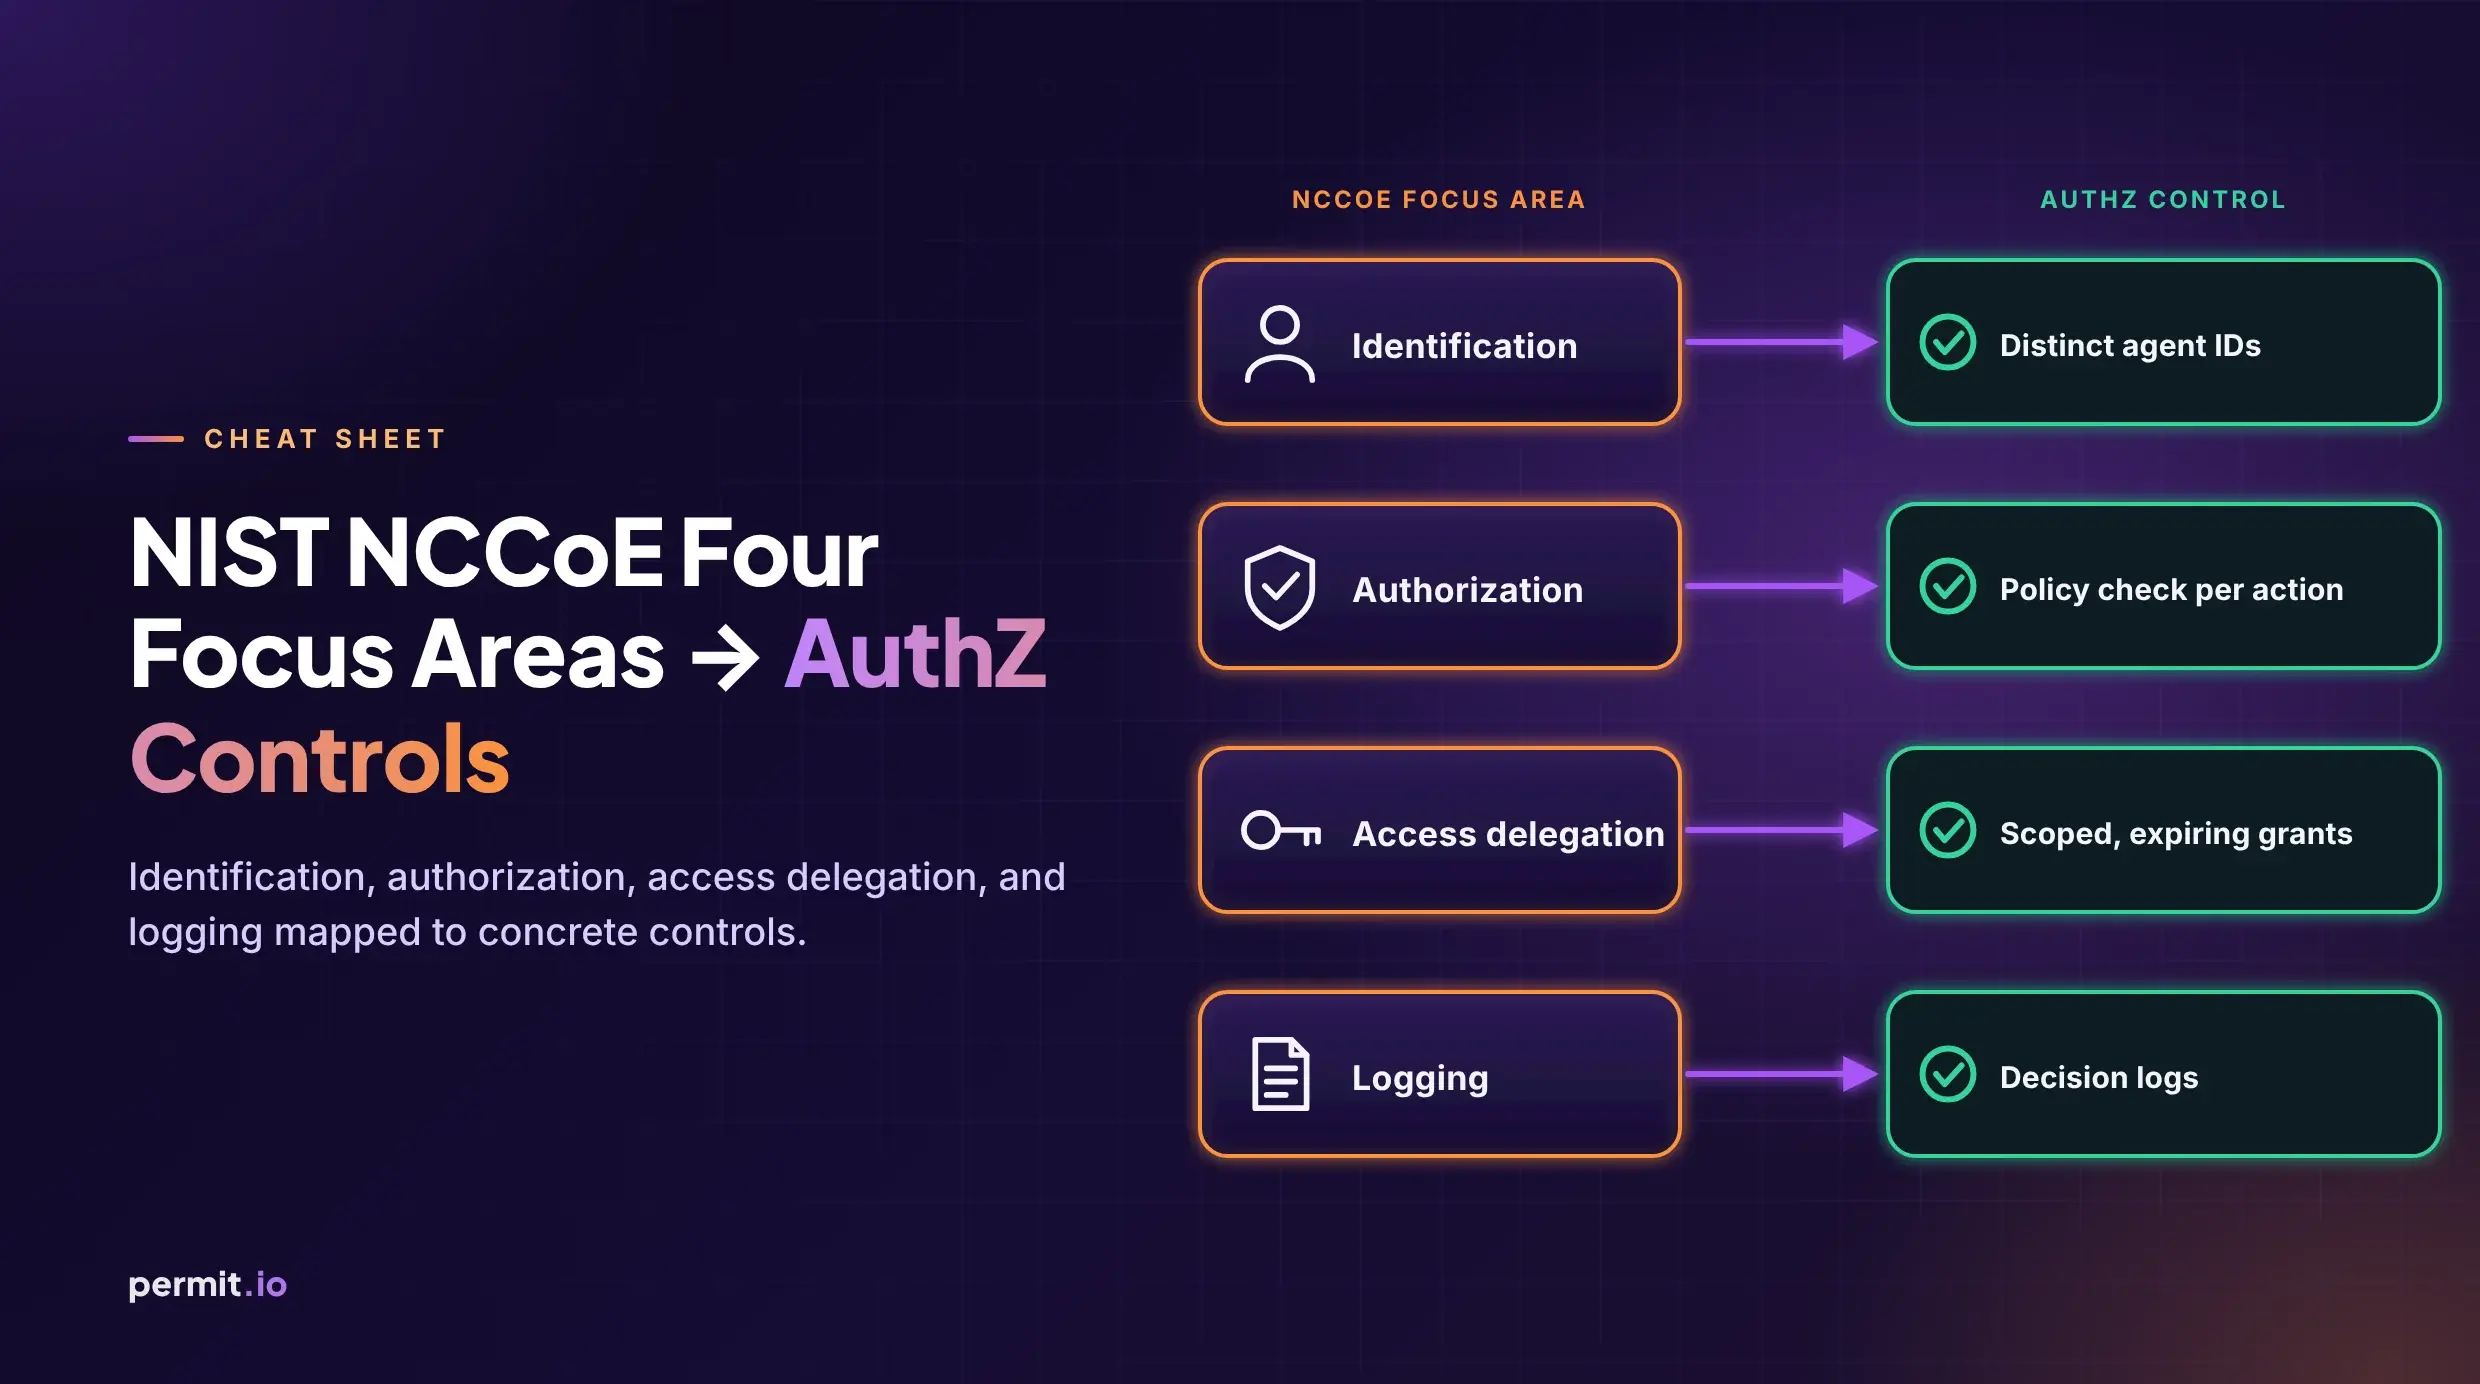
NIST NCCoE Four Focus Areas → AuthZ Controls
Cheat-sheet: NIST NCCoE's four focus areas (identification, authorization, access delegation, and logging) mapped to concrete AuthZ controls. Soft alignment aid, not a certification checklist.


Or Weis
Cheat-sheet: NIST NCCoE's four focus areas (identification, authorization, access delegation, and logging) mapped to concrete AuthZ controls. Soft alignment aid, not a certification checklist.

Or Weis
Treat AI agents as privileged NHIs: distinct identity, least privilege, attributable delegation, and forensic decision logs, not shared keys. Map to NIST NCCoE's identification · authorization · delegation · logging.

Or Weis
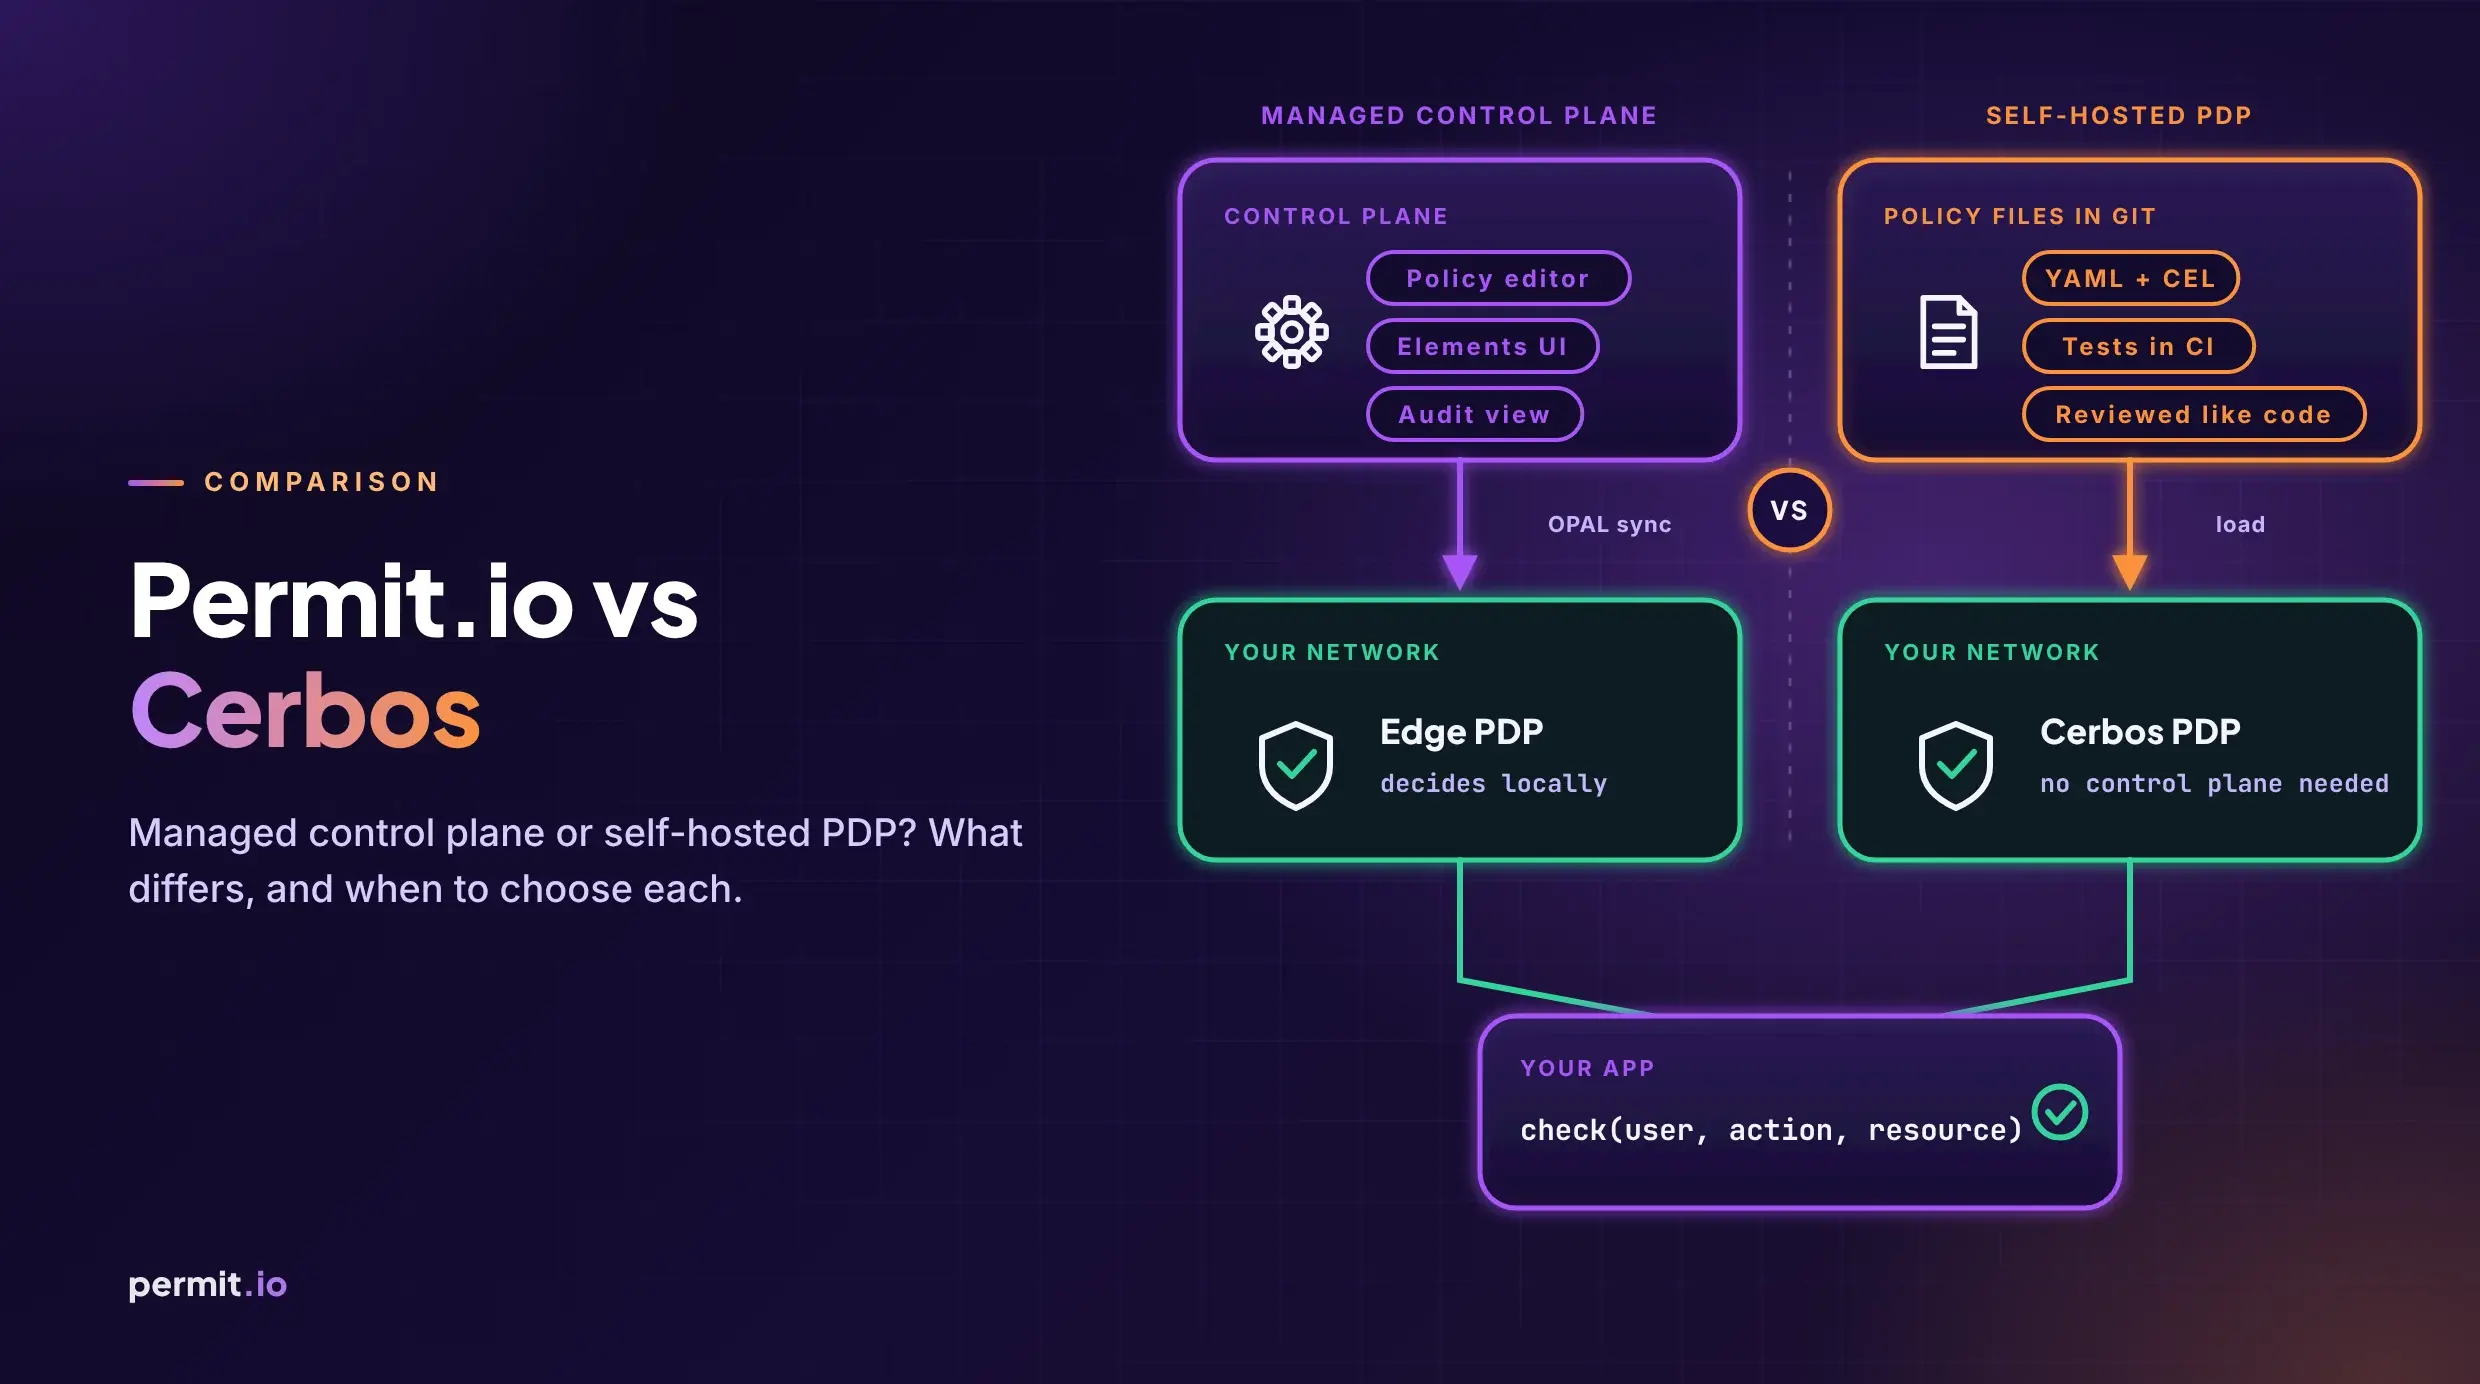
Permit.io and Cerbos can both run an open source policy decision point next to your app. A neutral comparison of managed control plane vs self-hosted PDP, with a table and when to choose each.

Or Weis
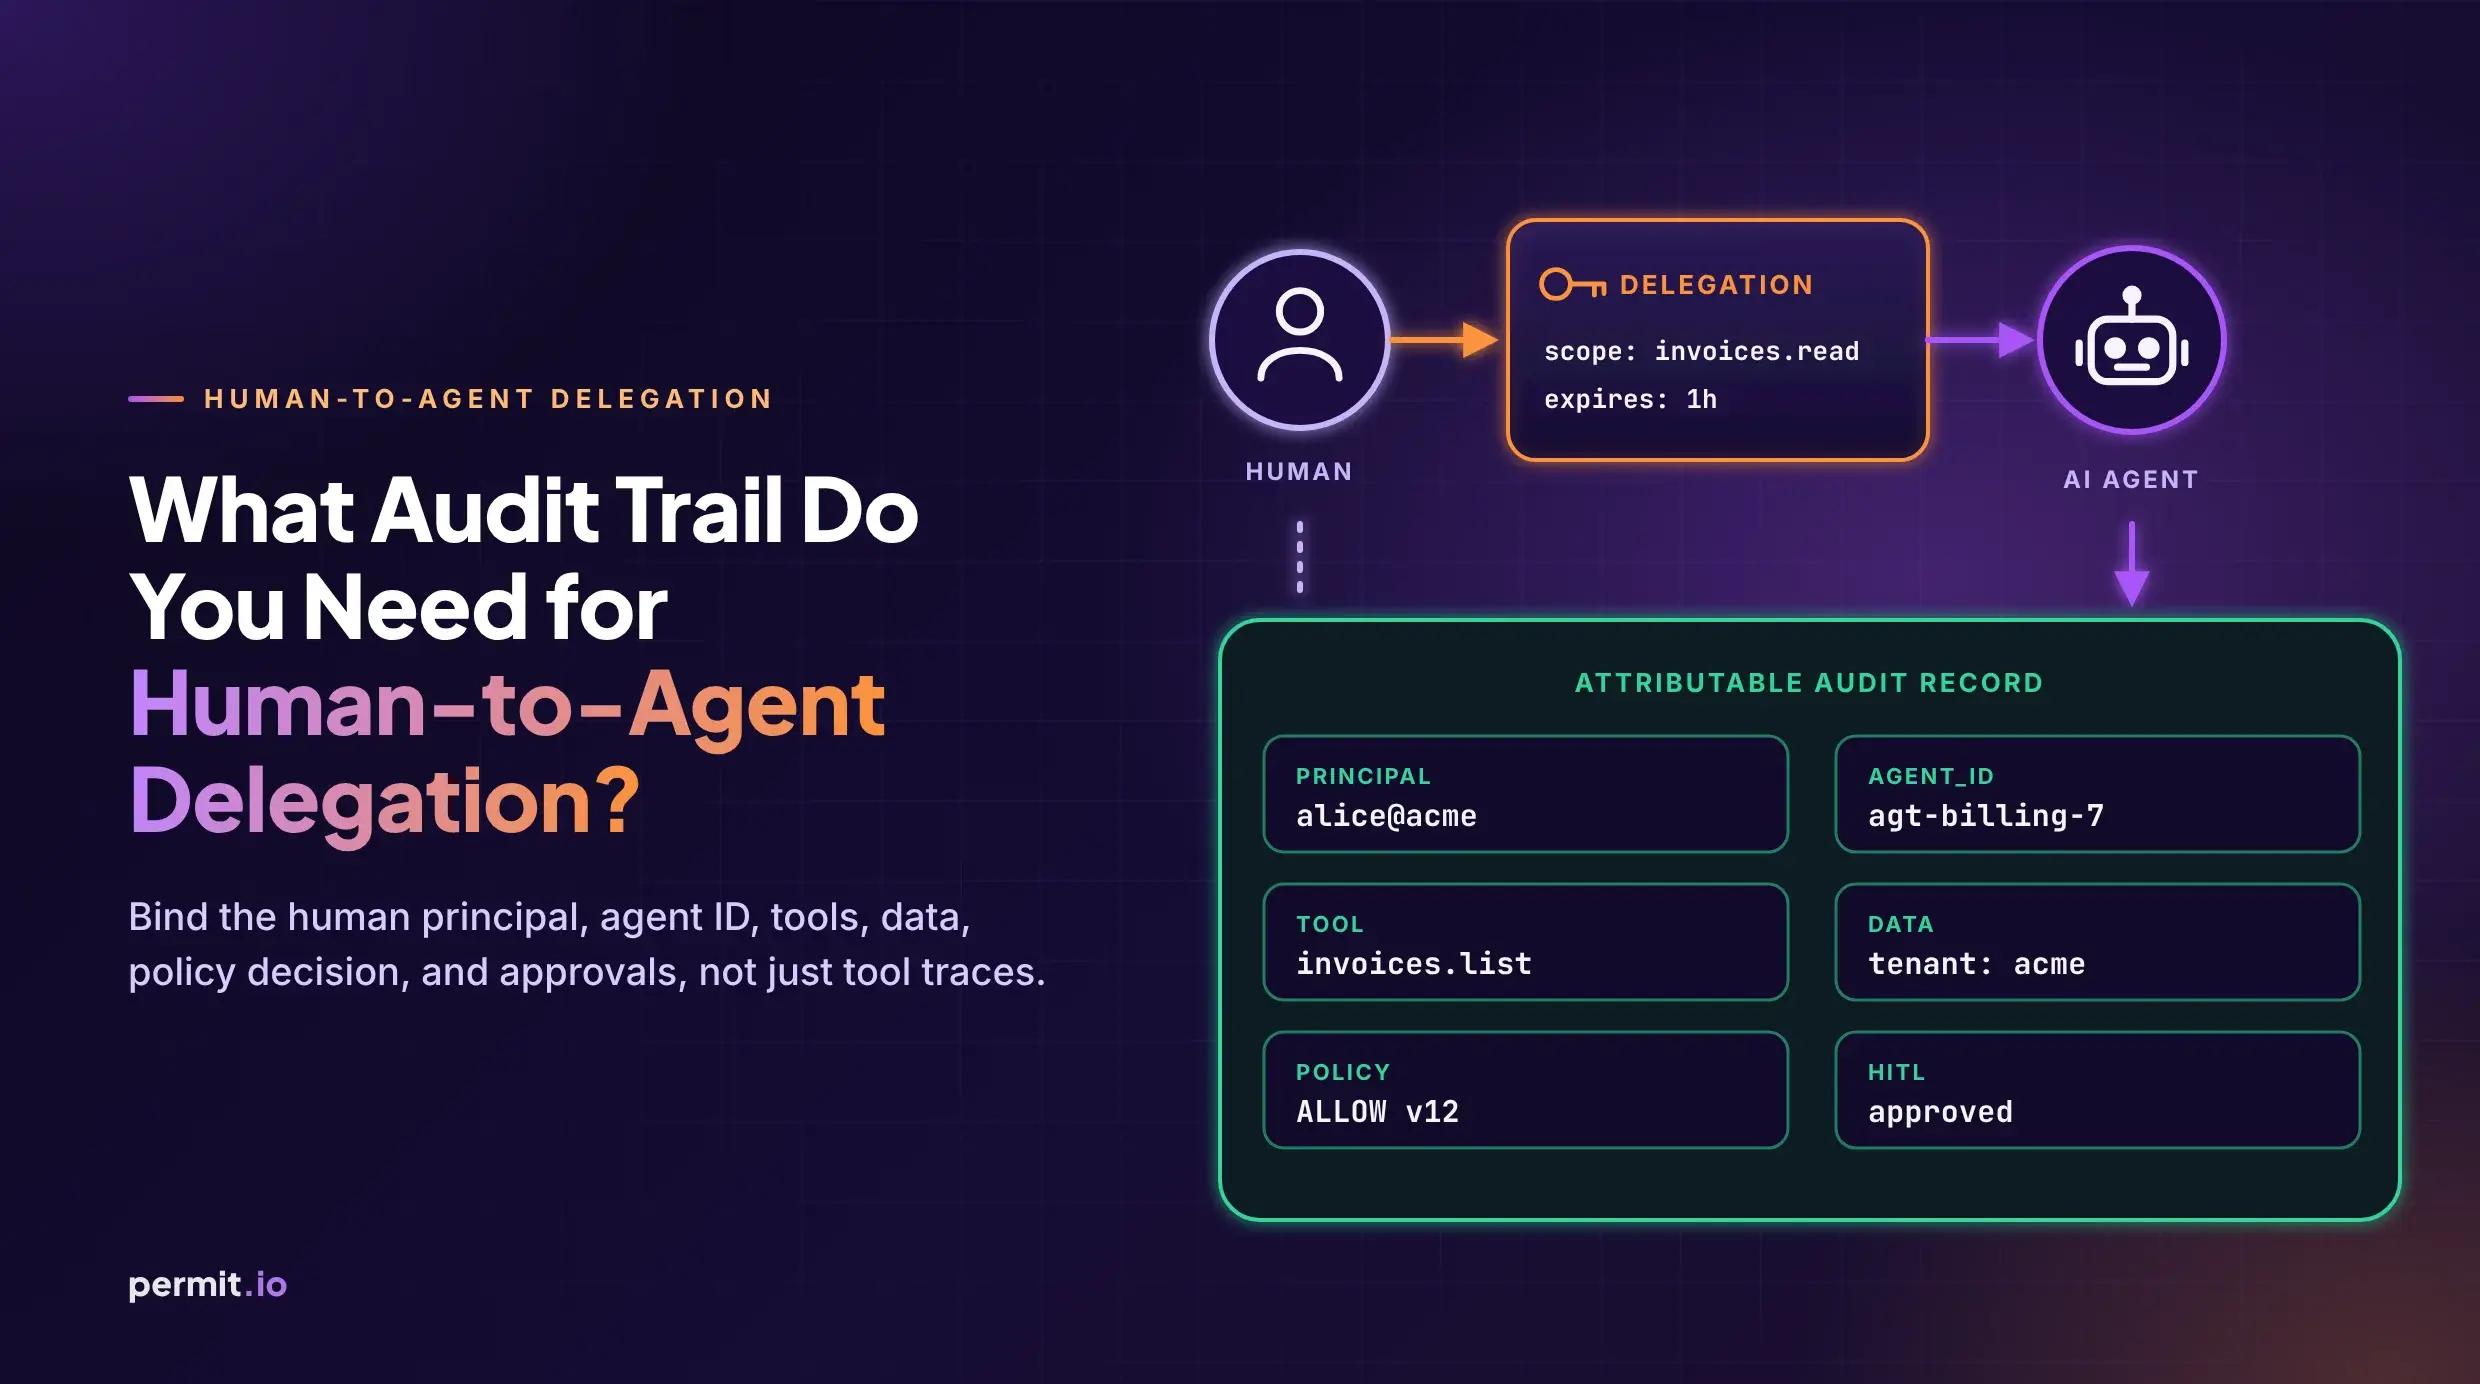
For human-to-agent delegation, bind human principal, agent ID, tools, data, policy decision, and HITL, not just tool traces, into an attributable audit trail.

Or Weis
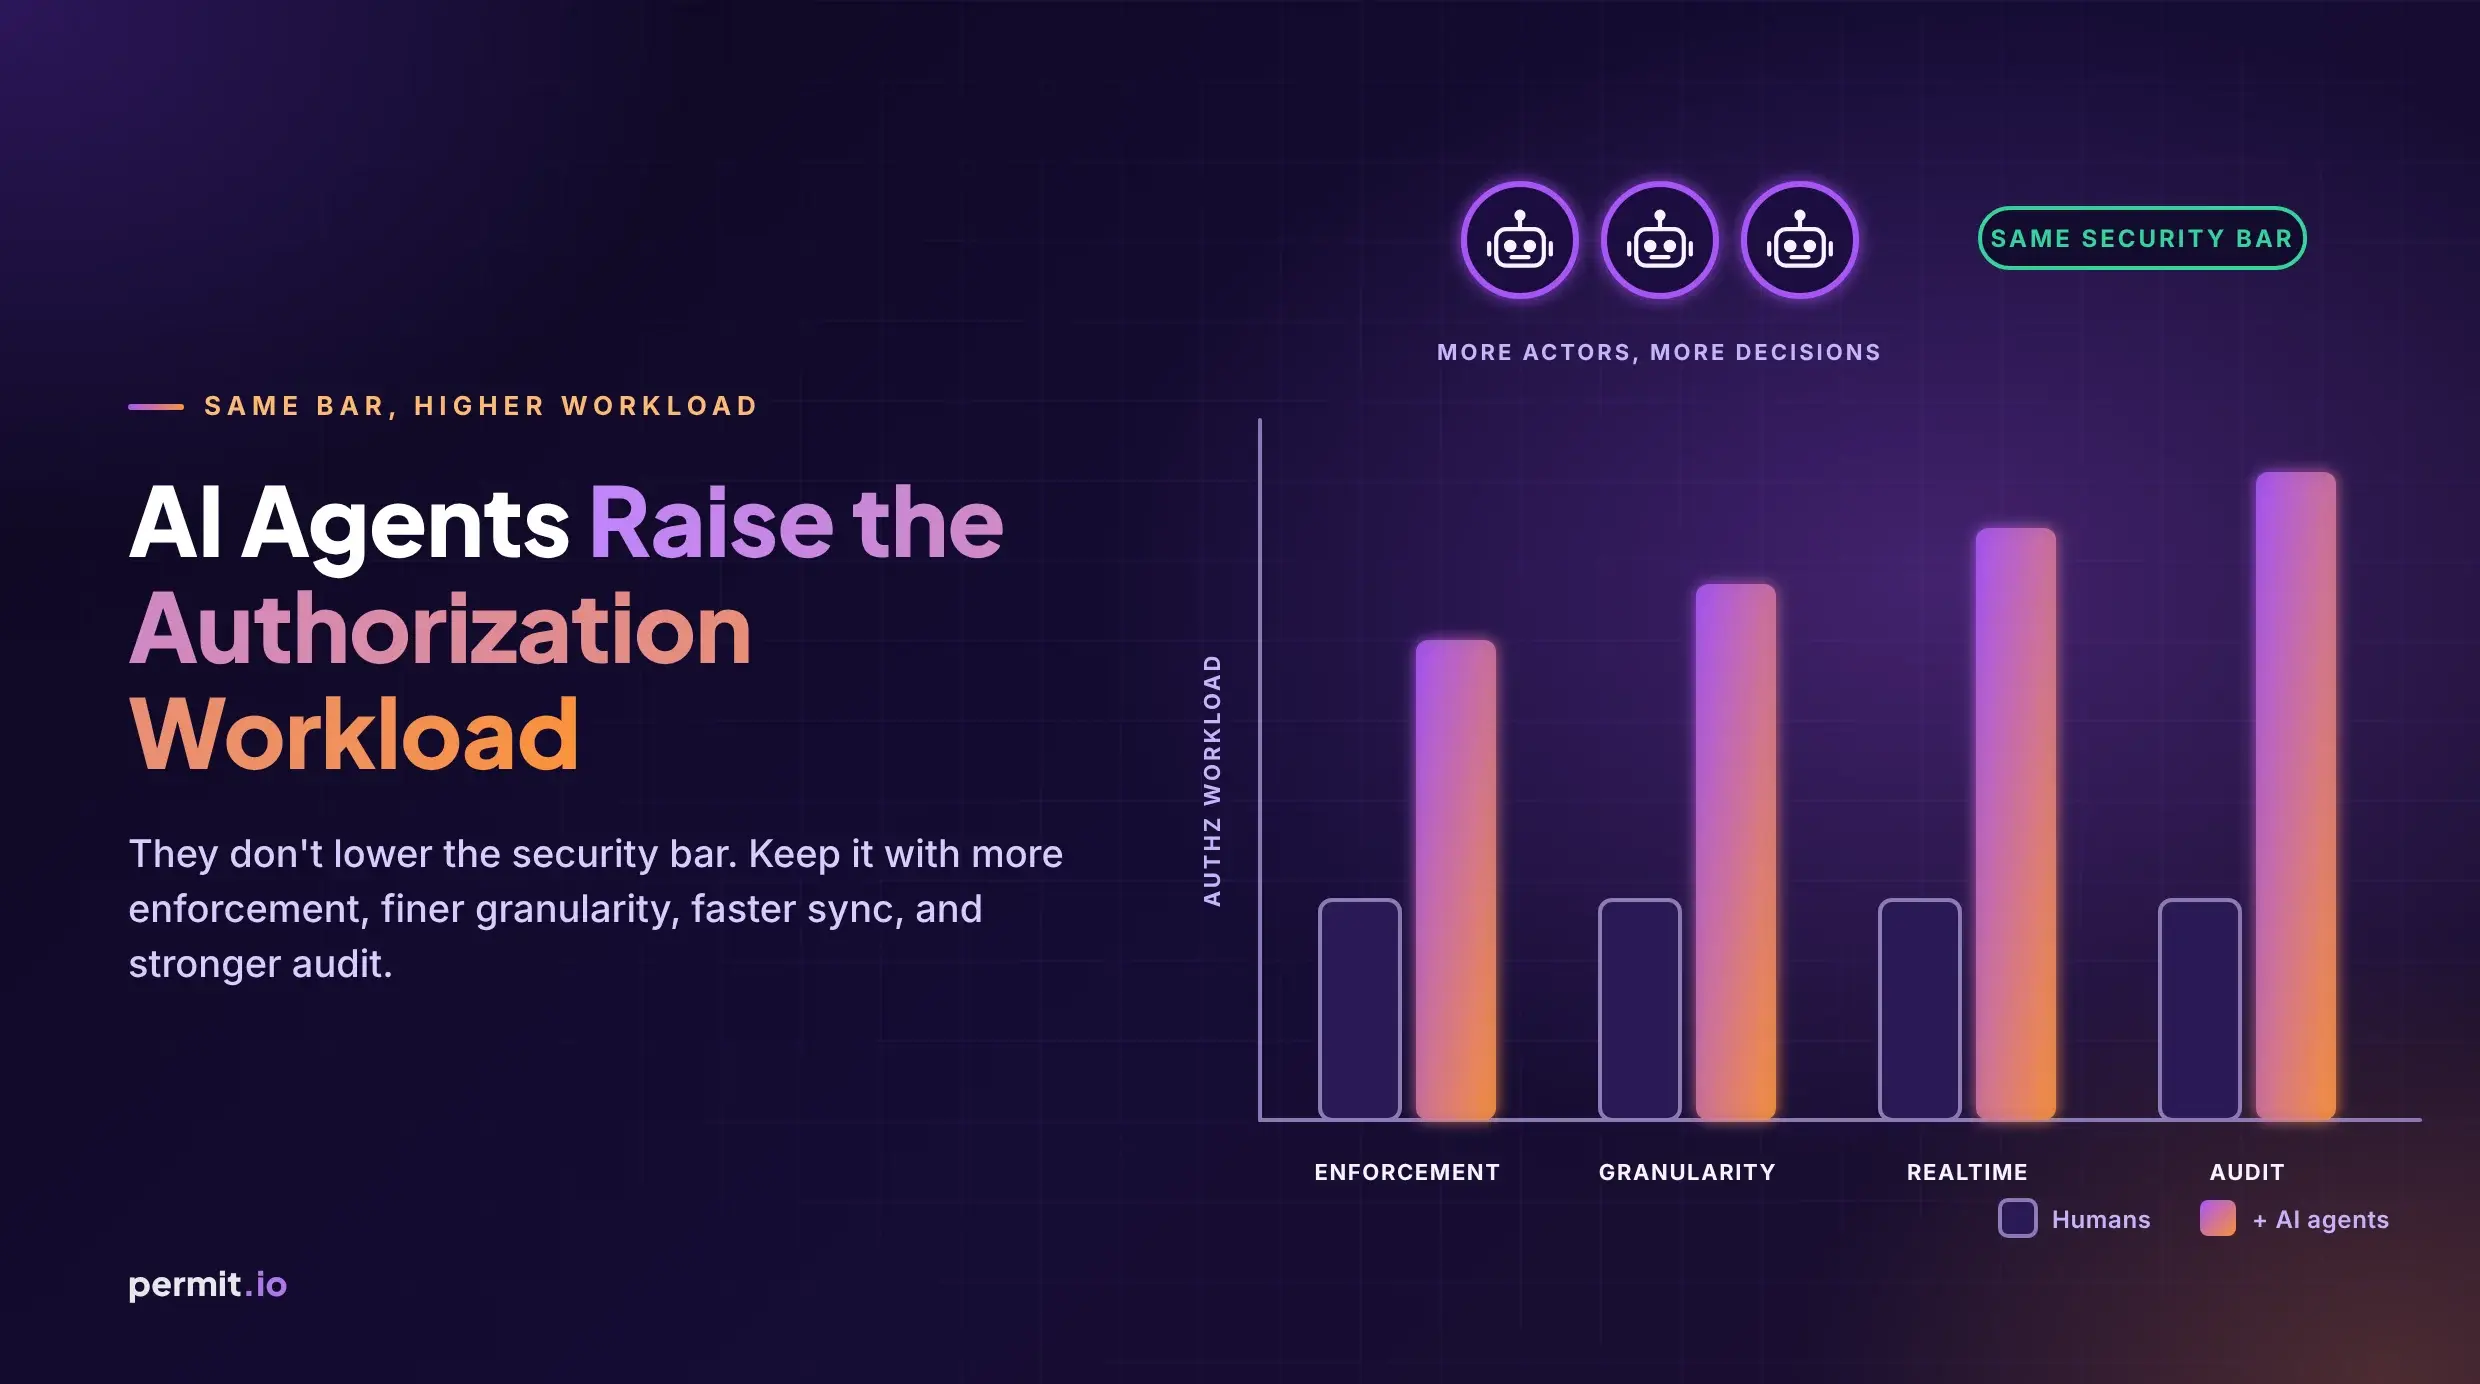
AI agents multiply the places where authorization must run. Delegation becomes a first-class part of the authorization shape: the human, the agent, the scope, the resource, conditions. Extend fine-grained authorization with per-action checks, trust ceilings, drift detection, and decision logs that explain what happened.

Or Weis
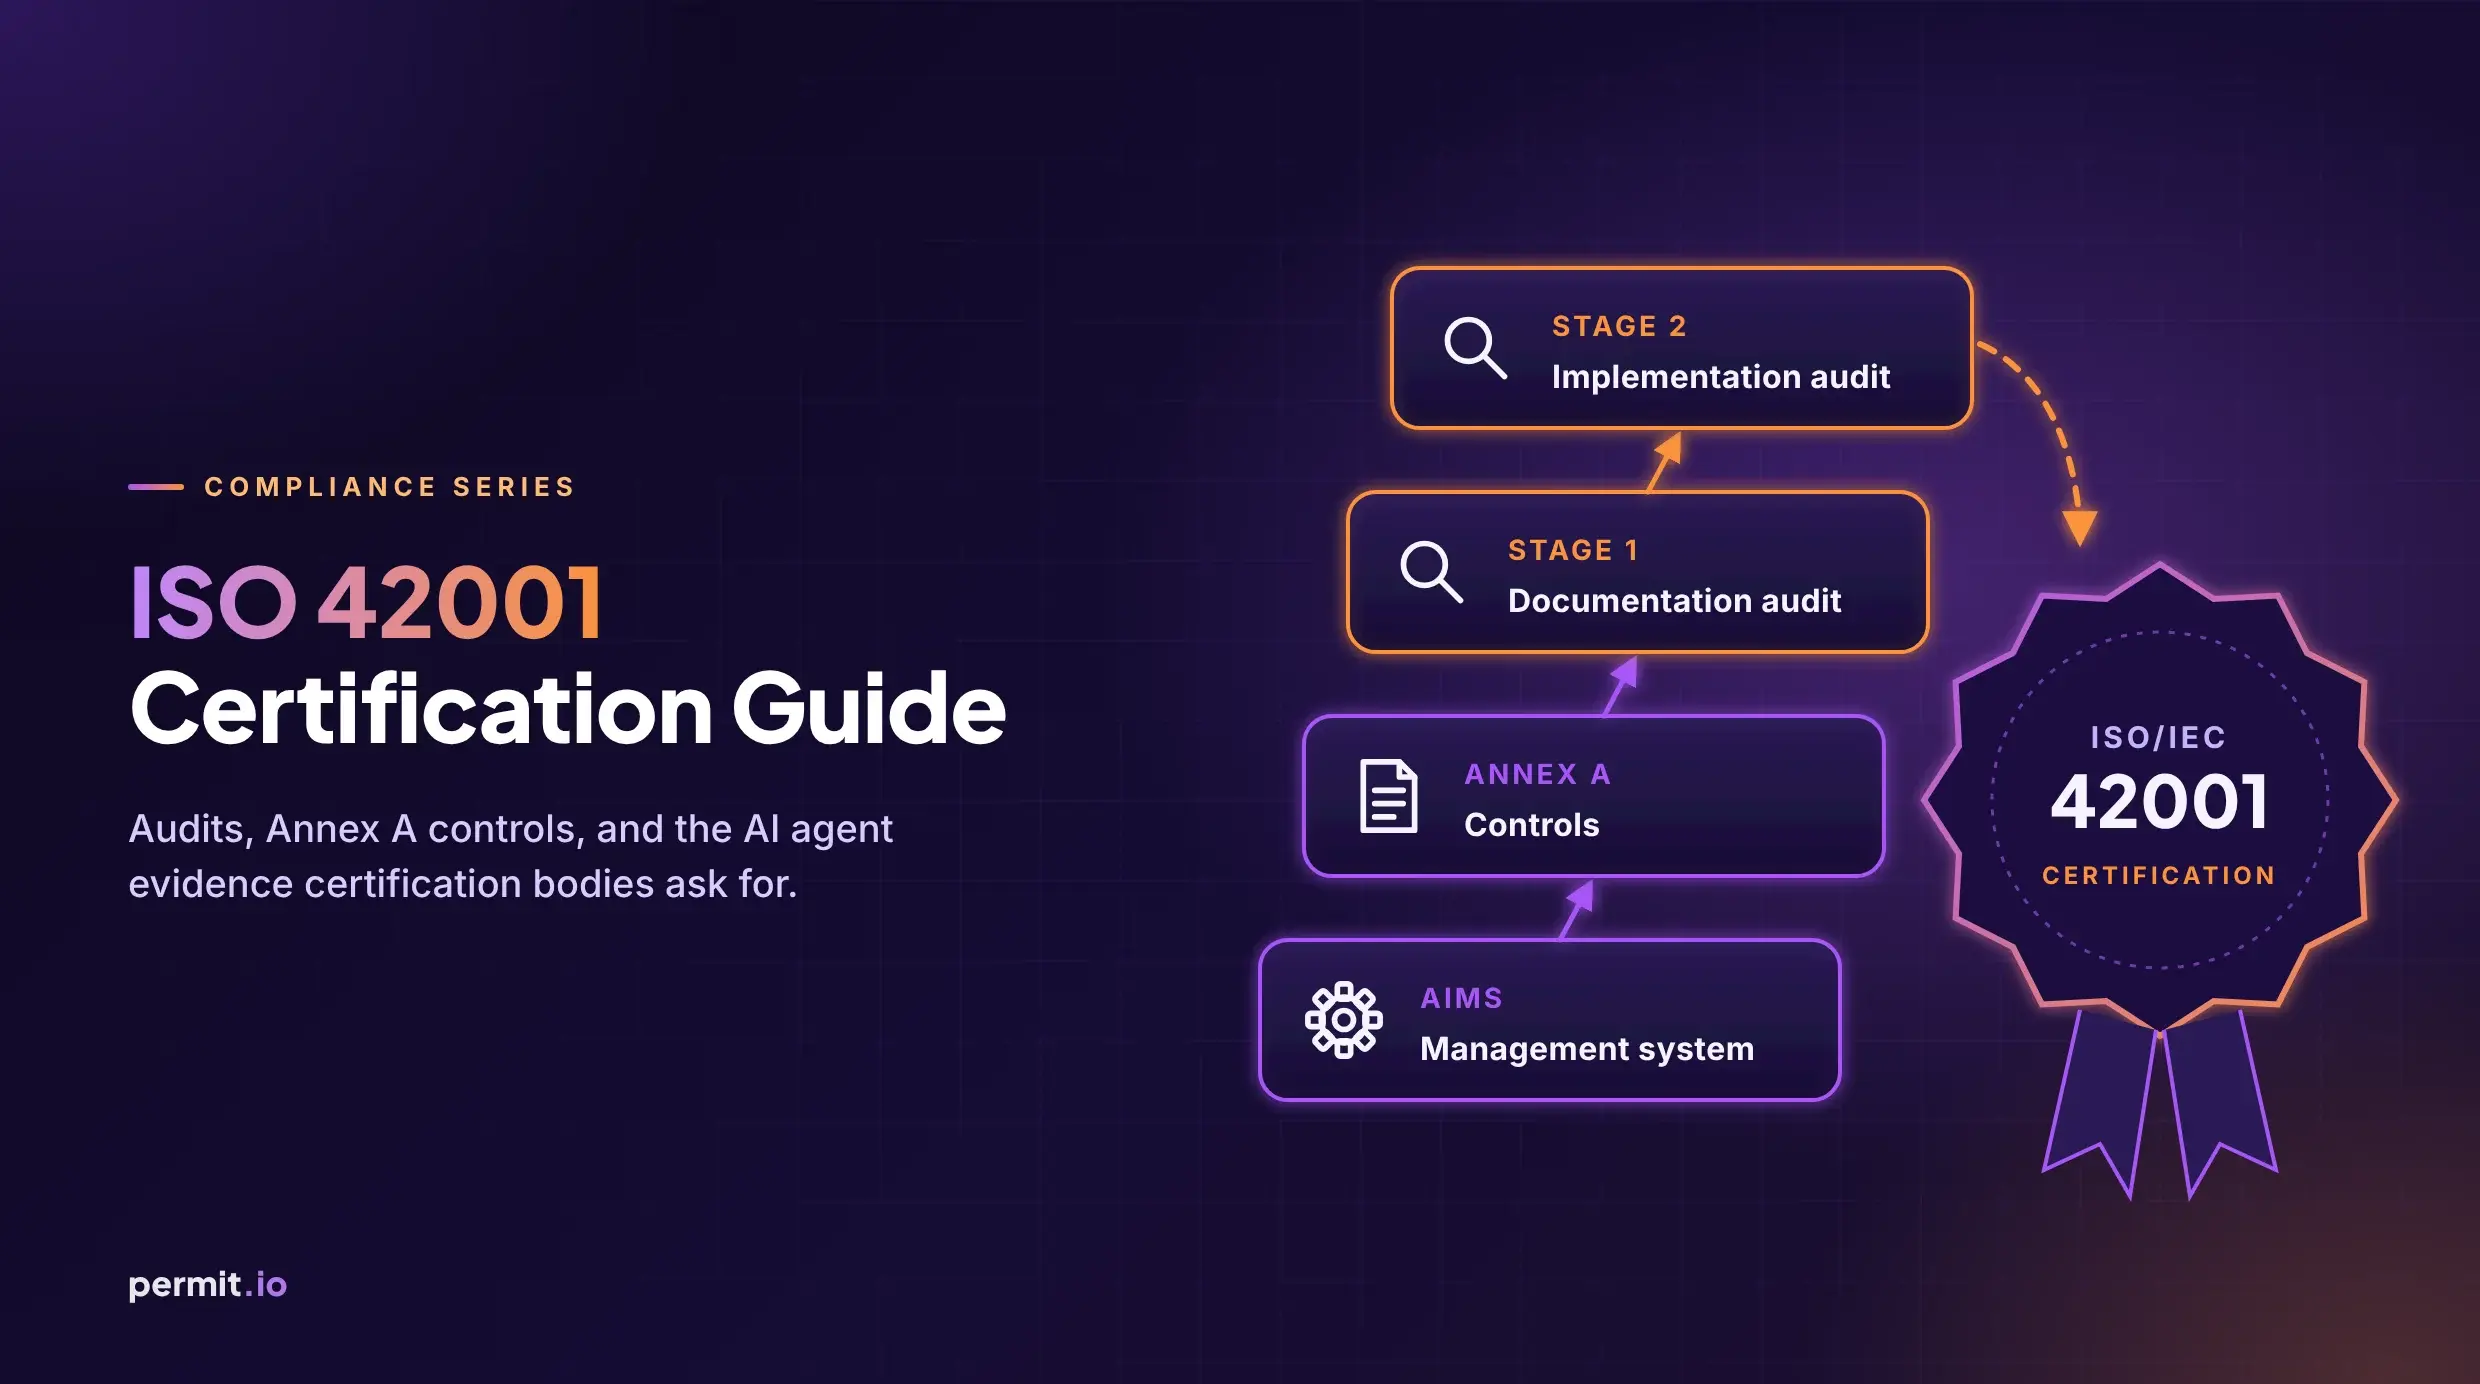
What ISO 42001 certification involves: the AI management system, accredited certification bodies, stage 1 and 2 audits, Annex A controls, and agent evidence.

Or Weis
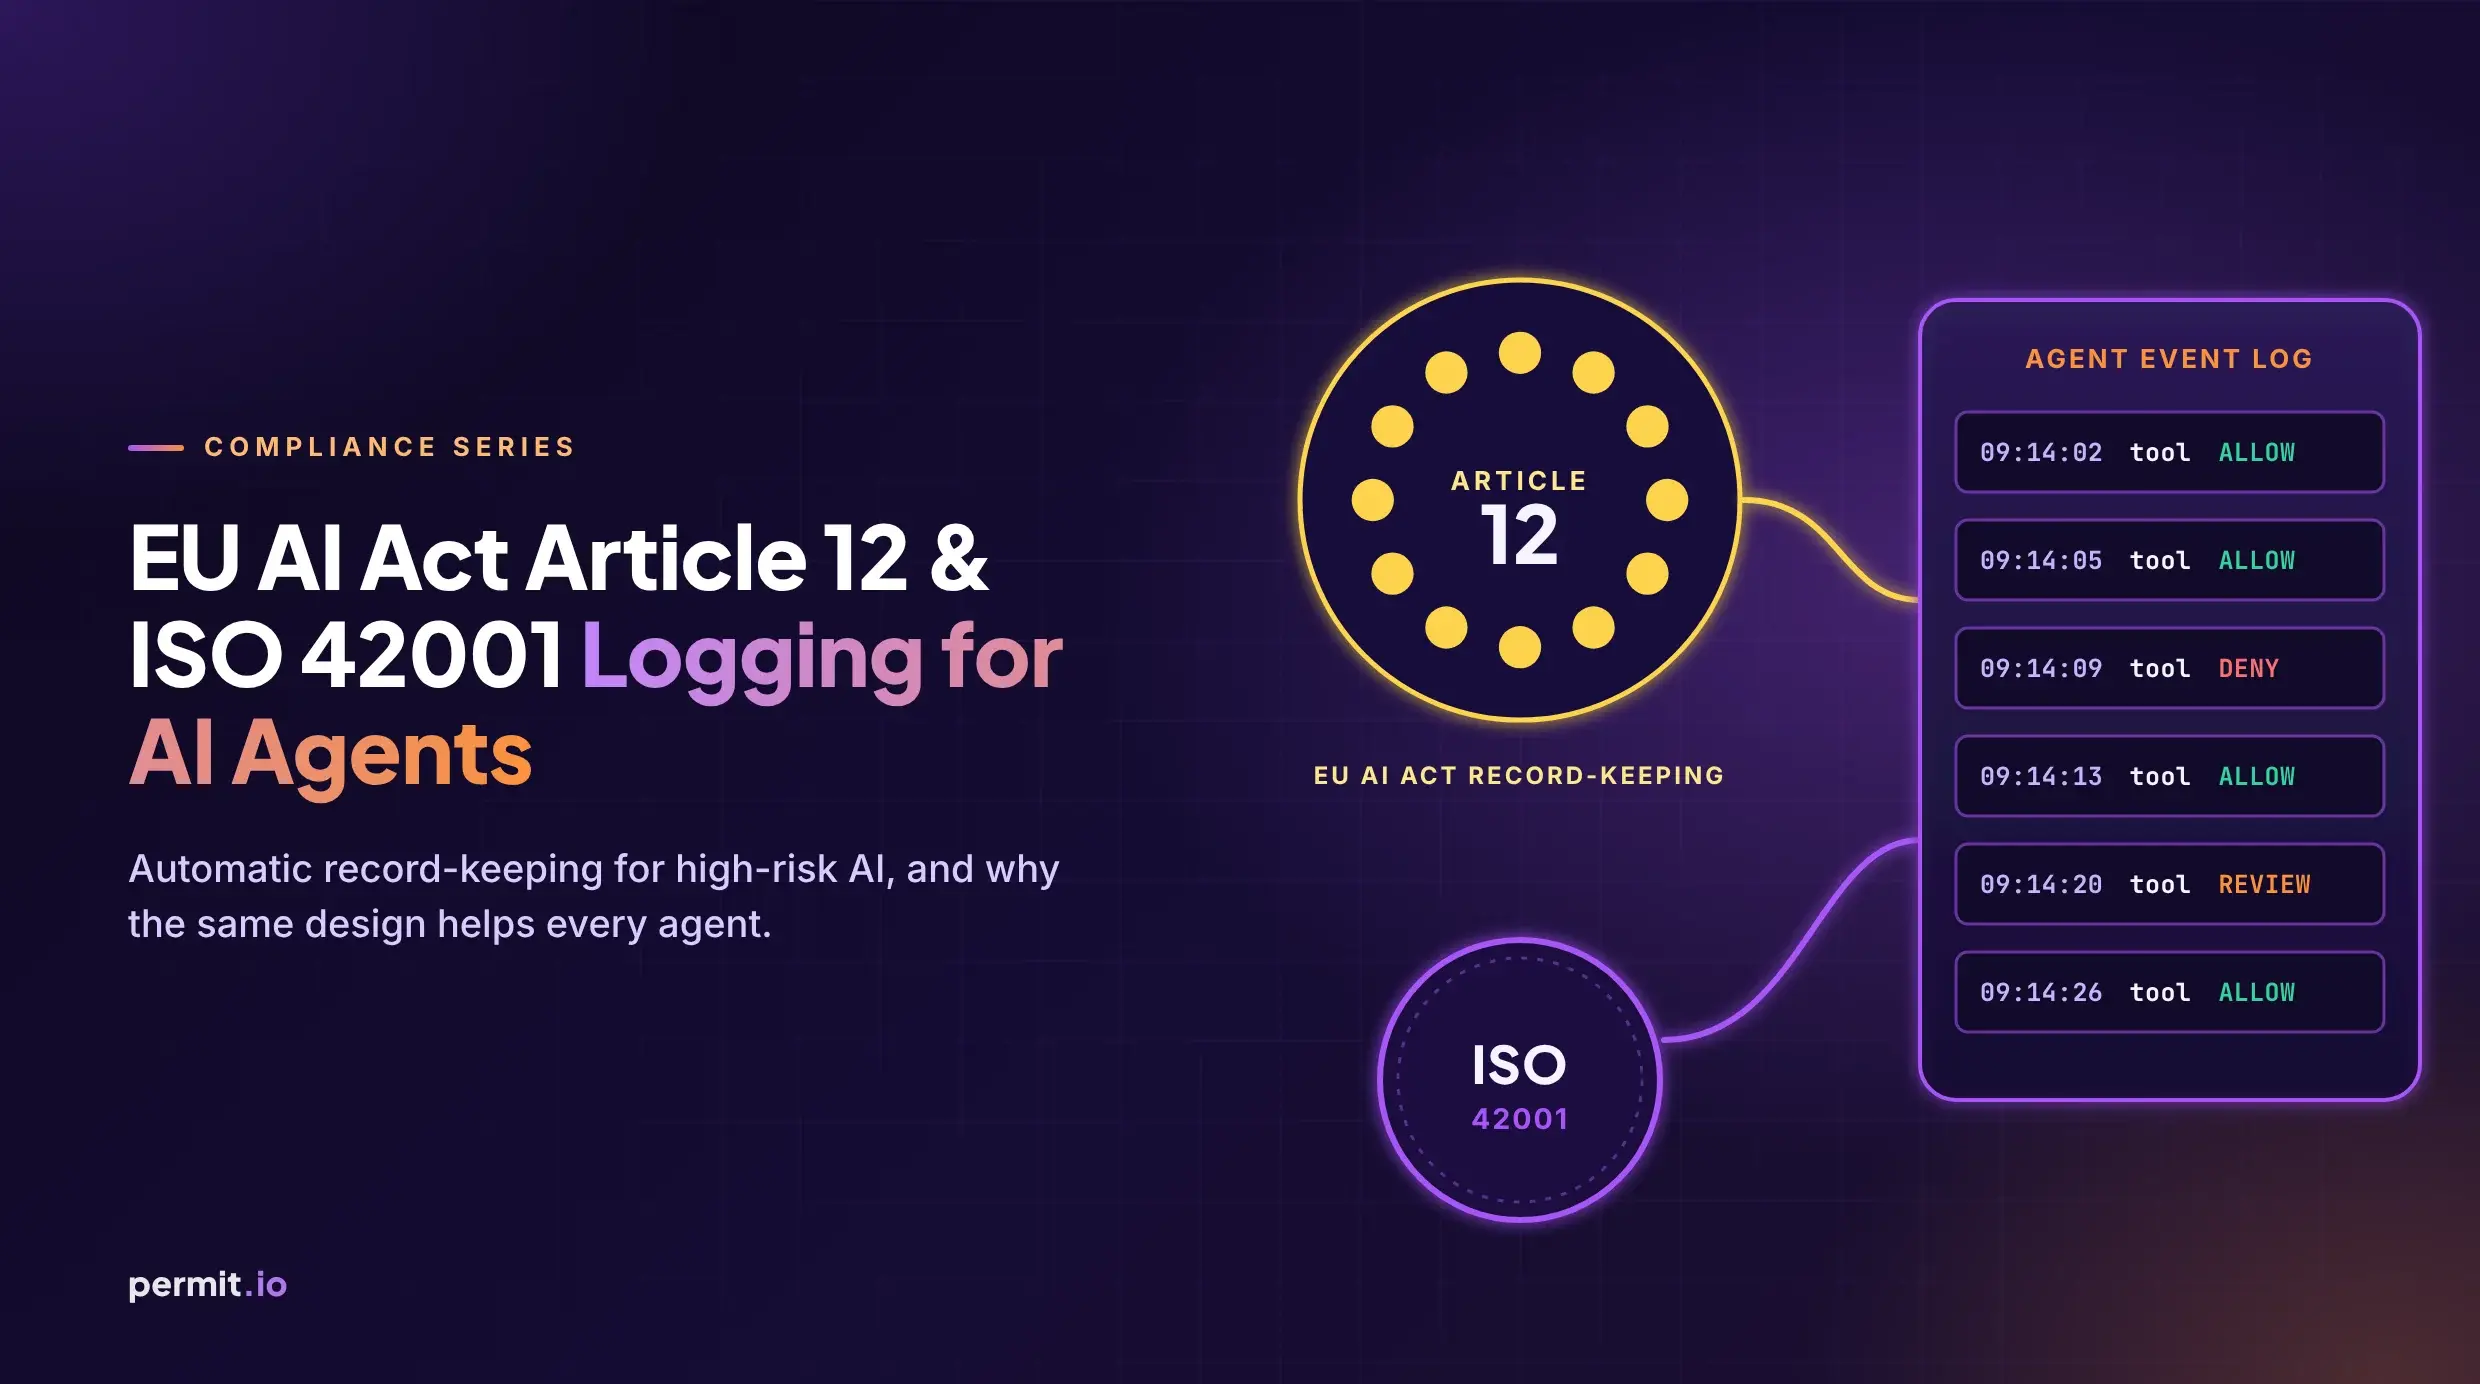
EU AI Act logging requirements under Article 12 for high-risk AI systems, log retention rules (at least six months for deployers under Article 26(6)), ISO 42001 A.6.2.8, and practical logging design for AI agents.

Or Weis
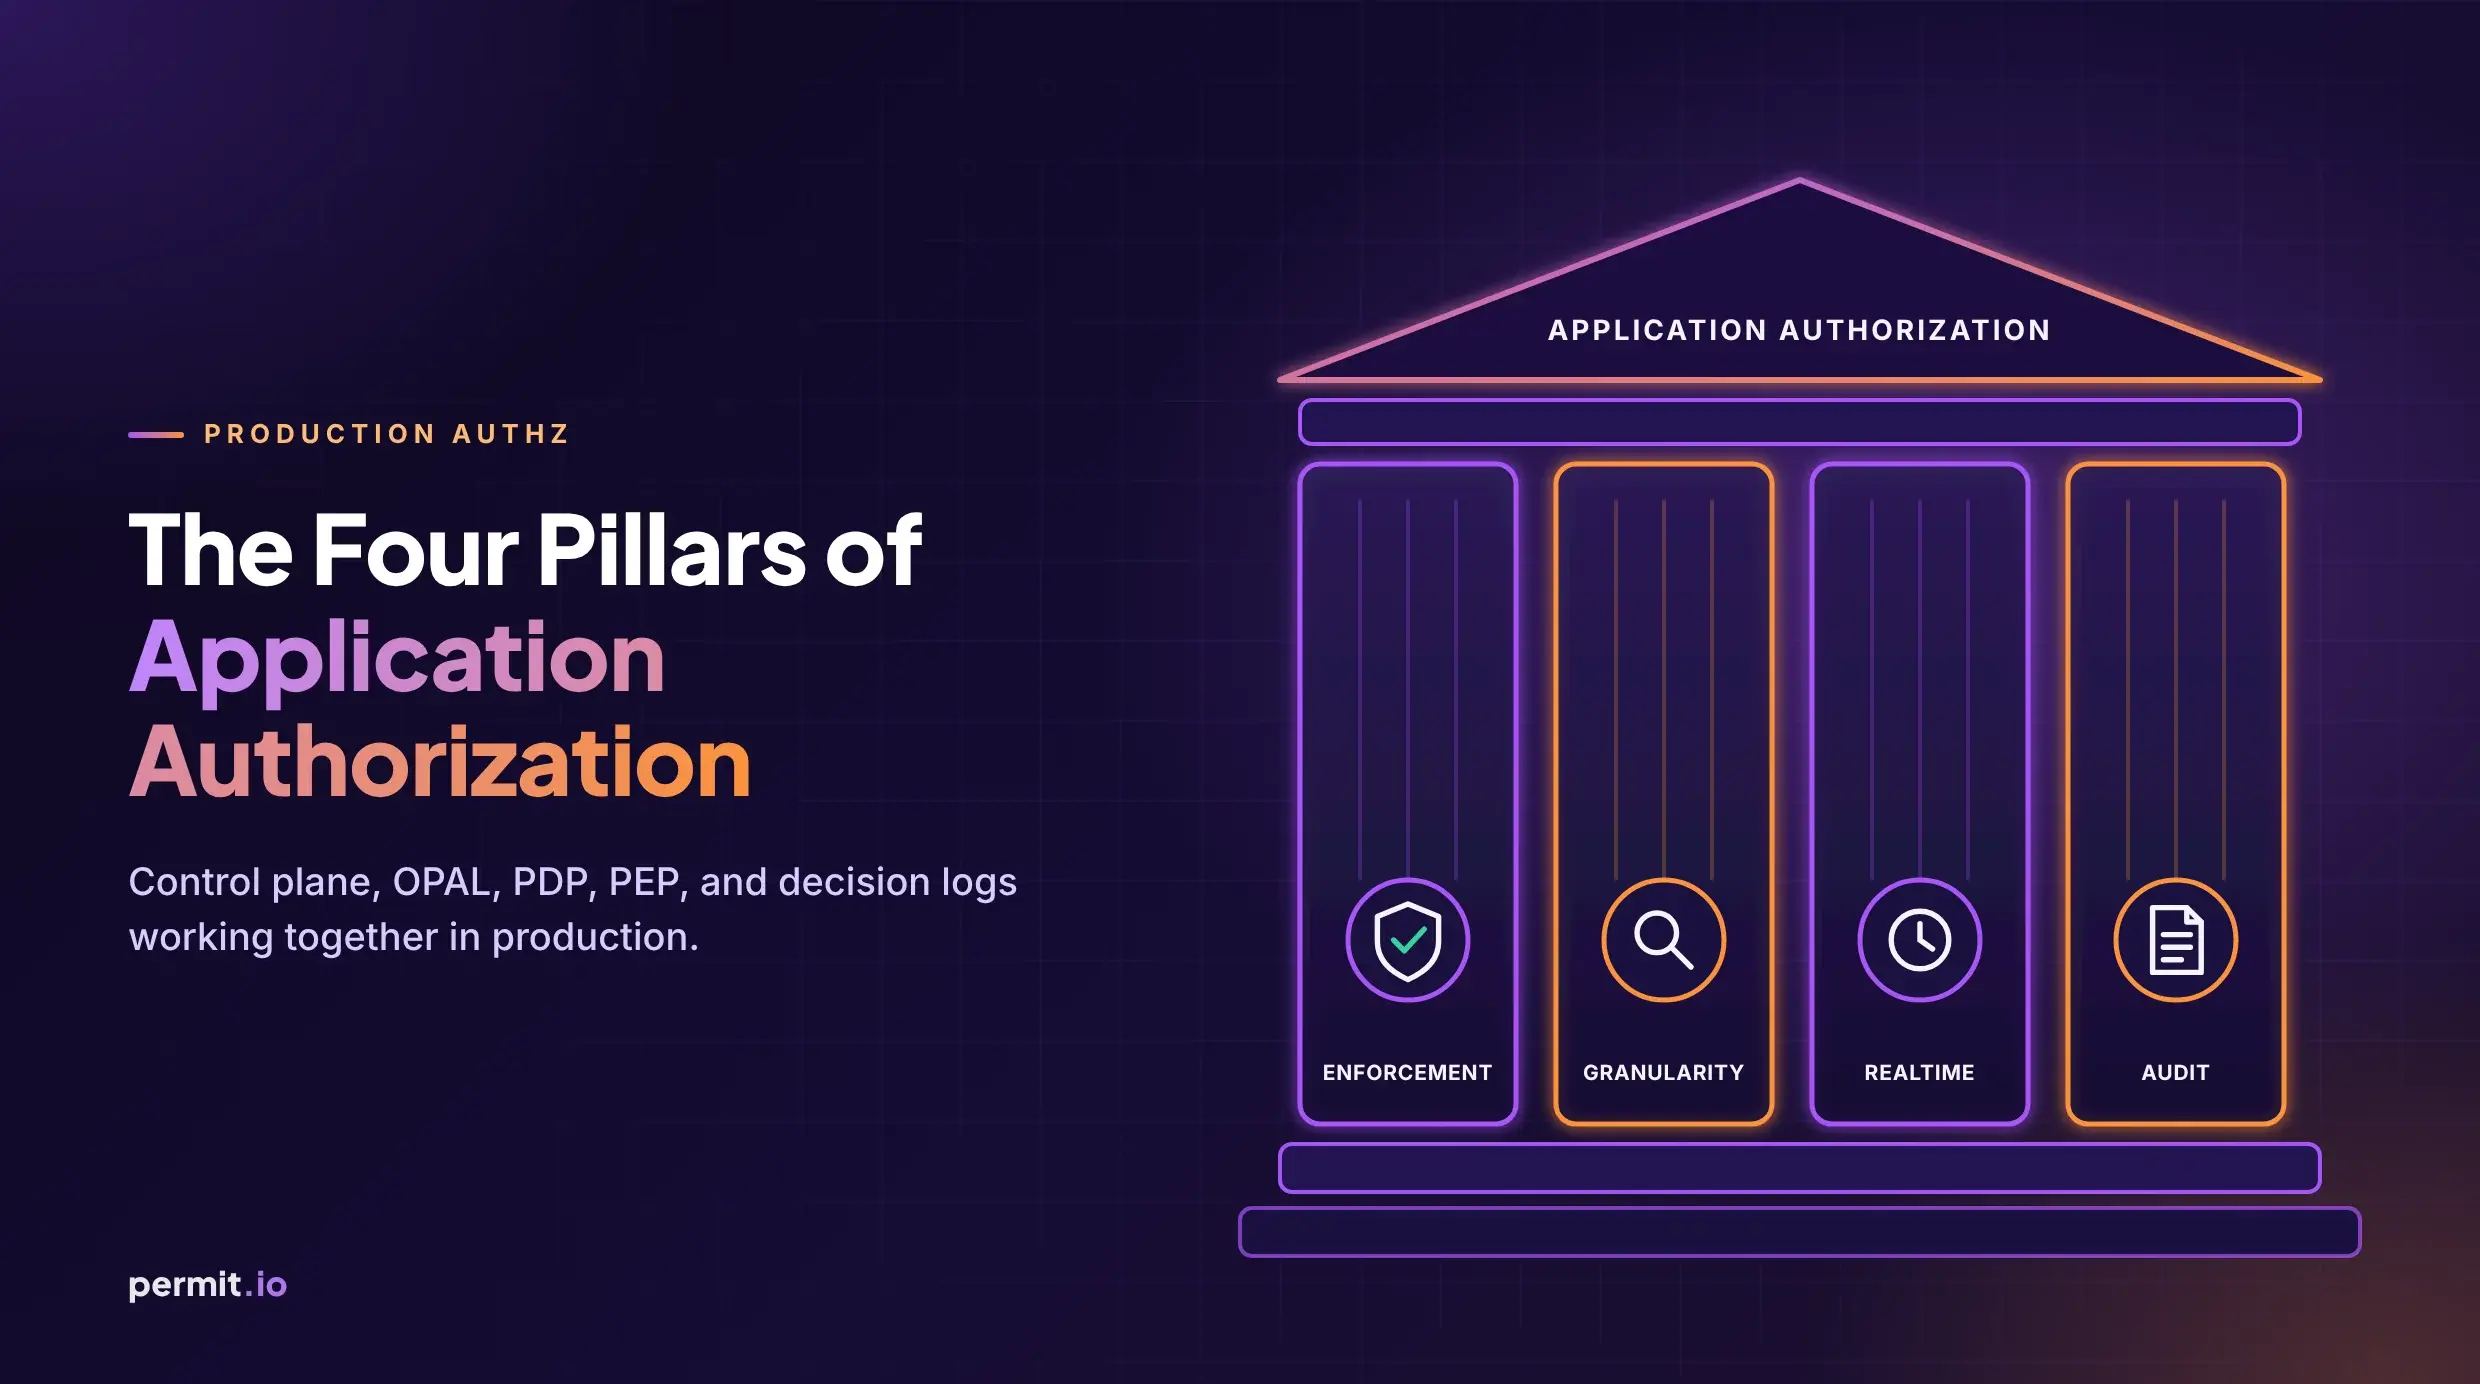
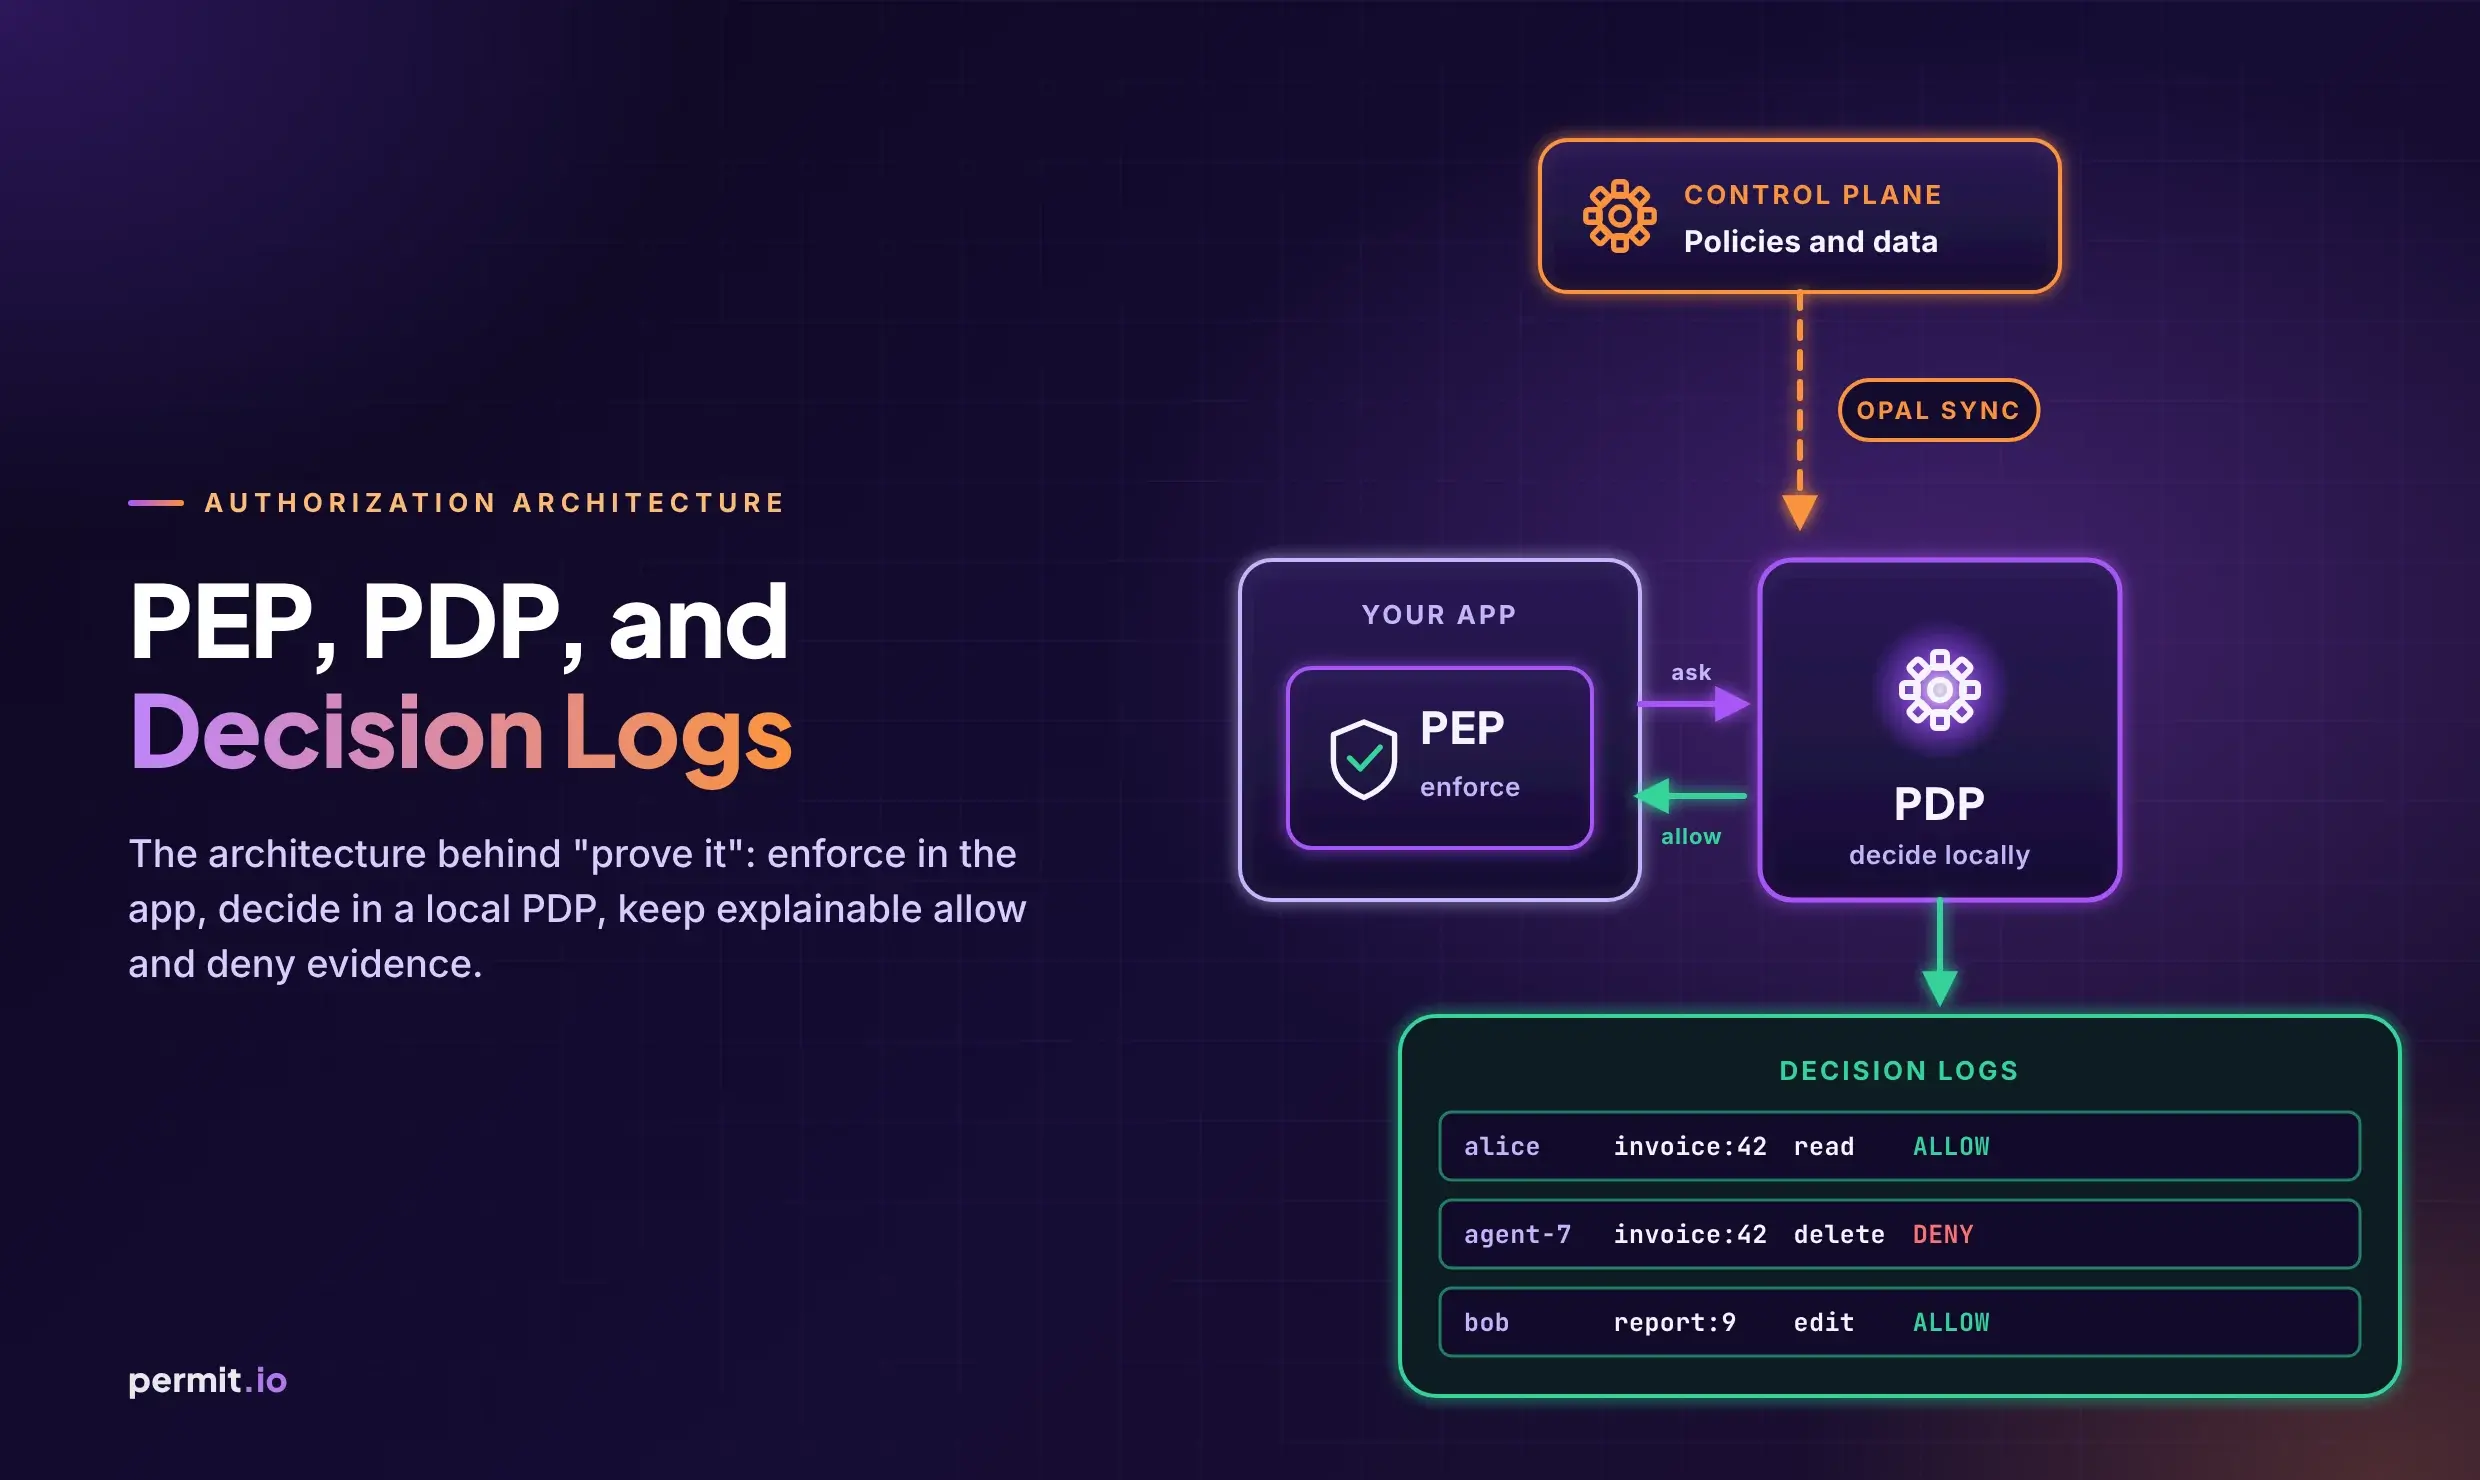
Production authorization enforcement requires four pillars: a policy decision at every sensitive action, granular policy models, realtime revocation, and auditable decisions. Control plane to OPAL to PDP to PEP to logs is the architecture that makes them work together.

Or Weis
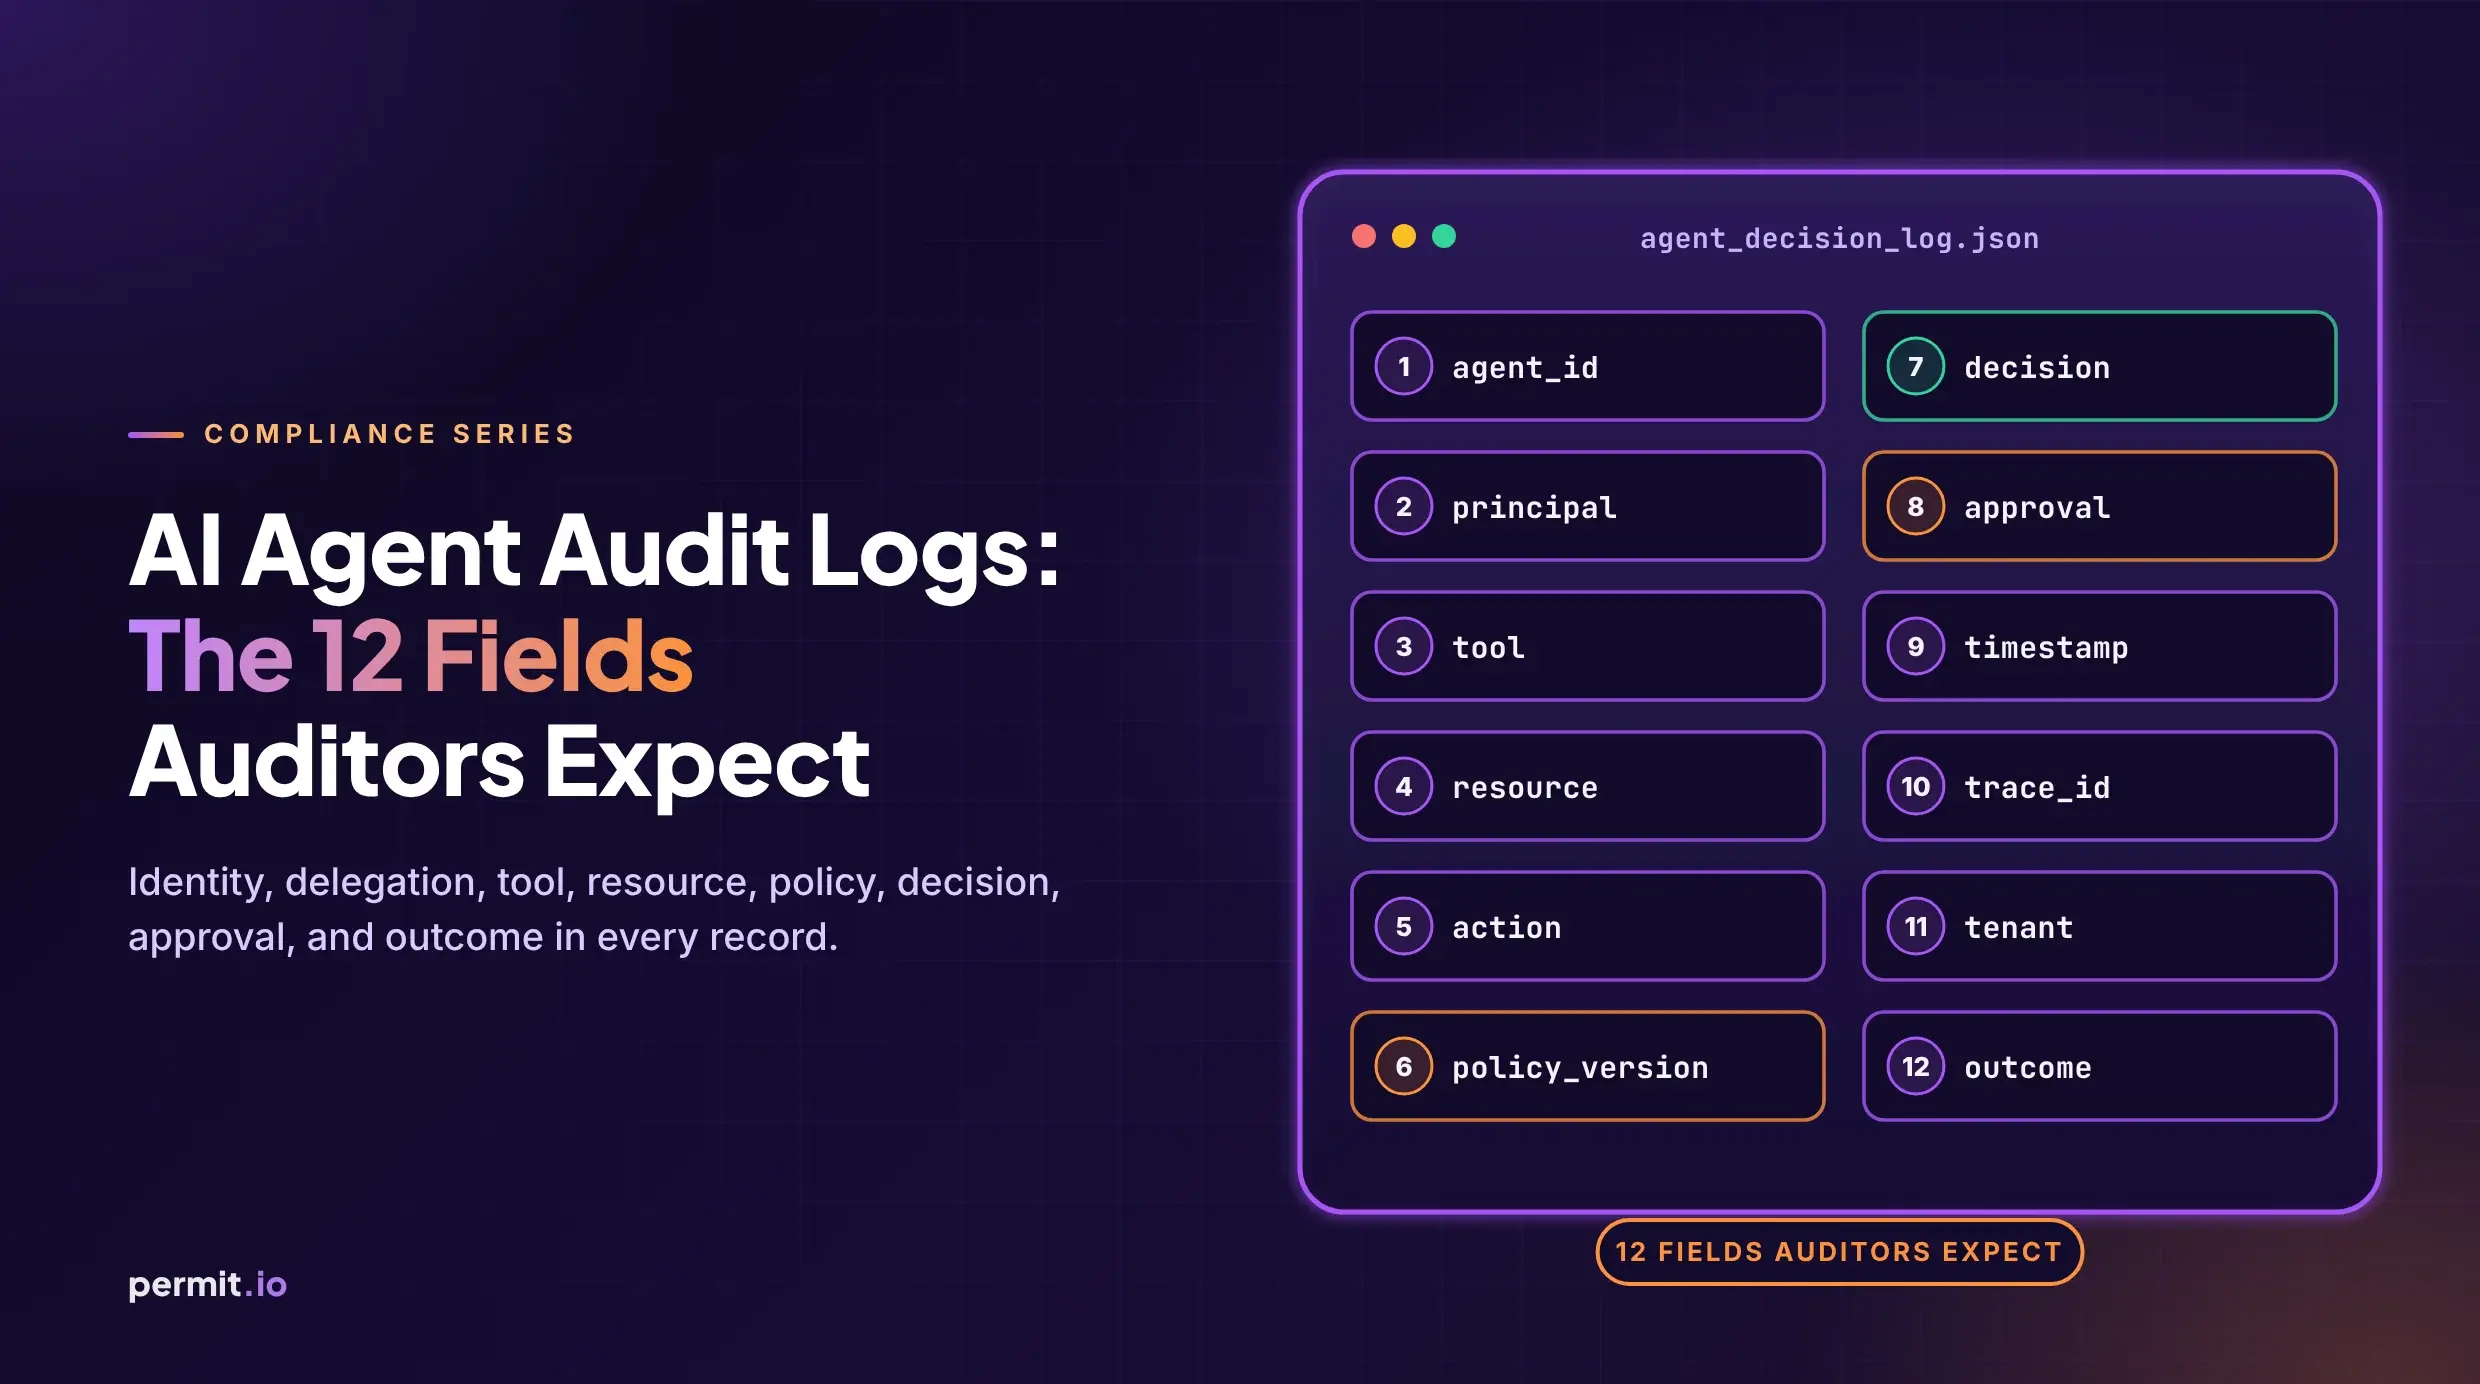
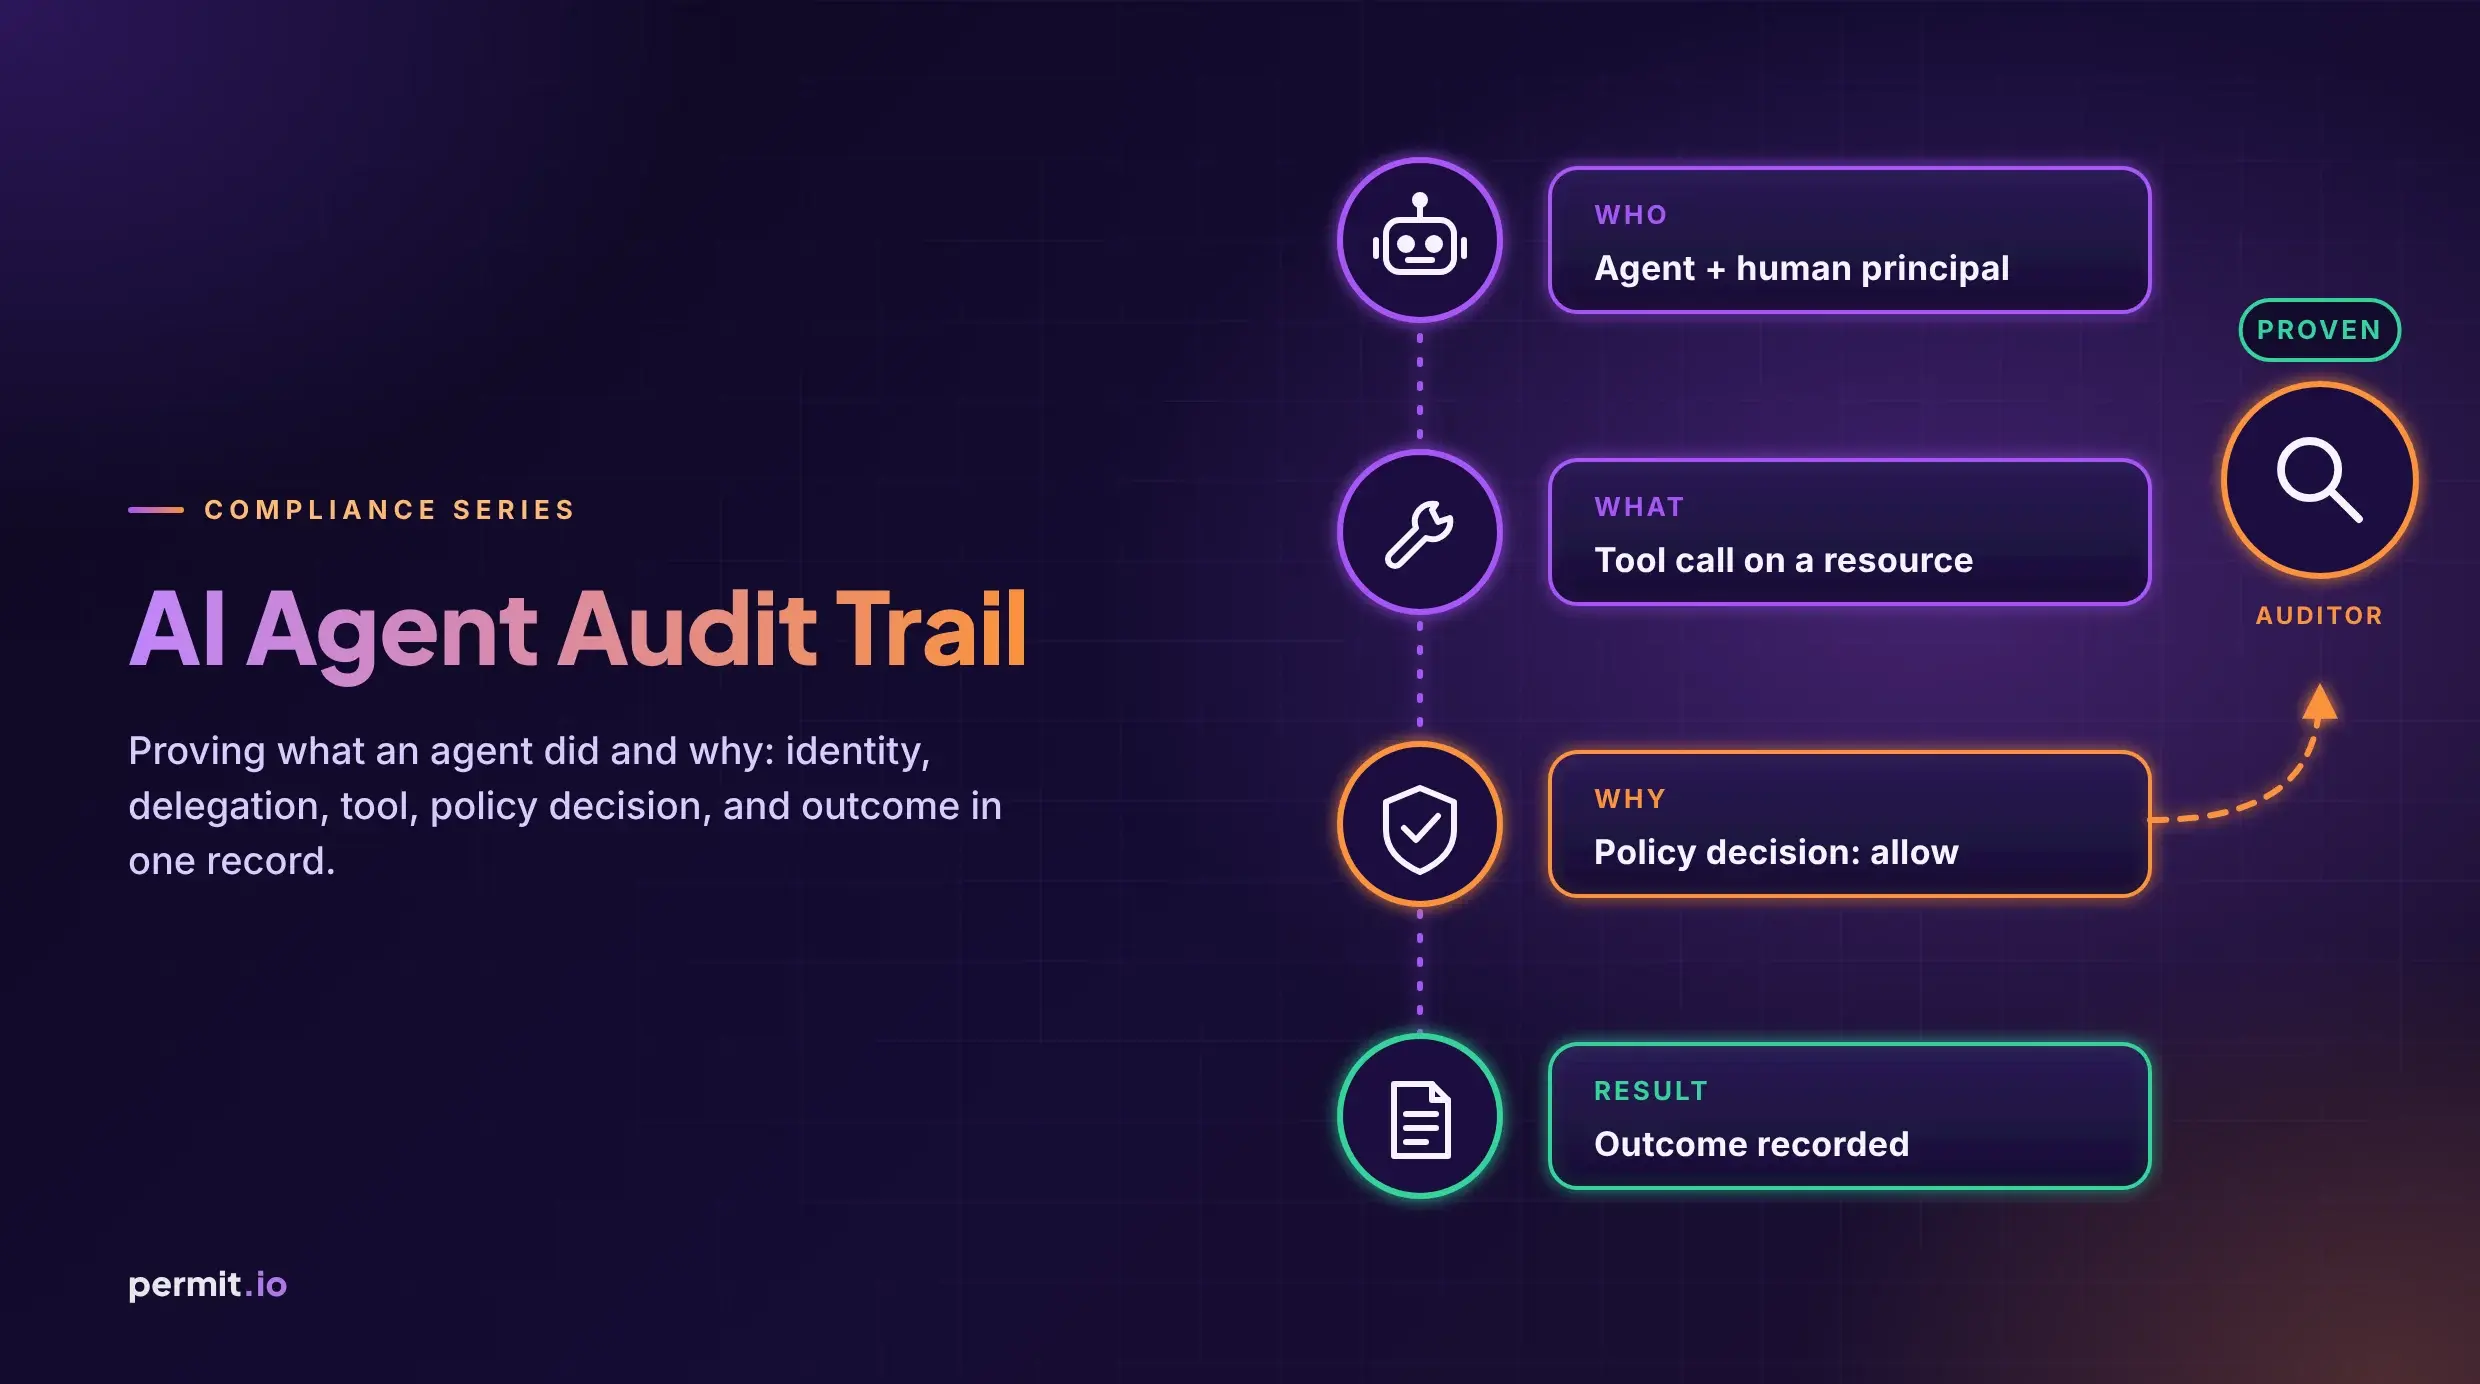
AI agent audit logs need about twelve fields: identity, delegation, tool, resource, policy, decision, HITL, and outcome.

Or Weis
An AI agent audit trail binds identity, delegation, tool, resource, policy, allow/deny, HITL, and outcome. Tool traces are not enough.

Or Weis
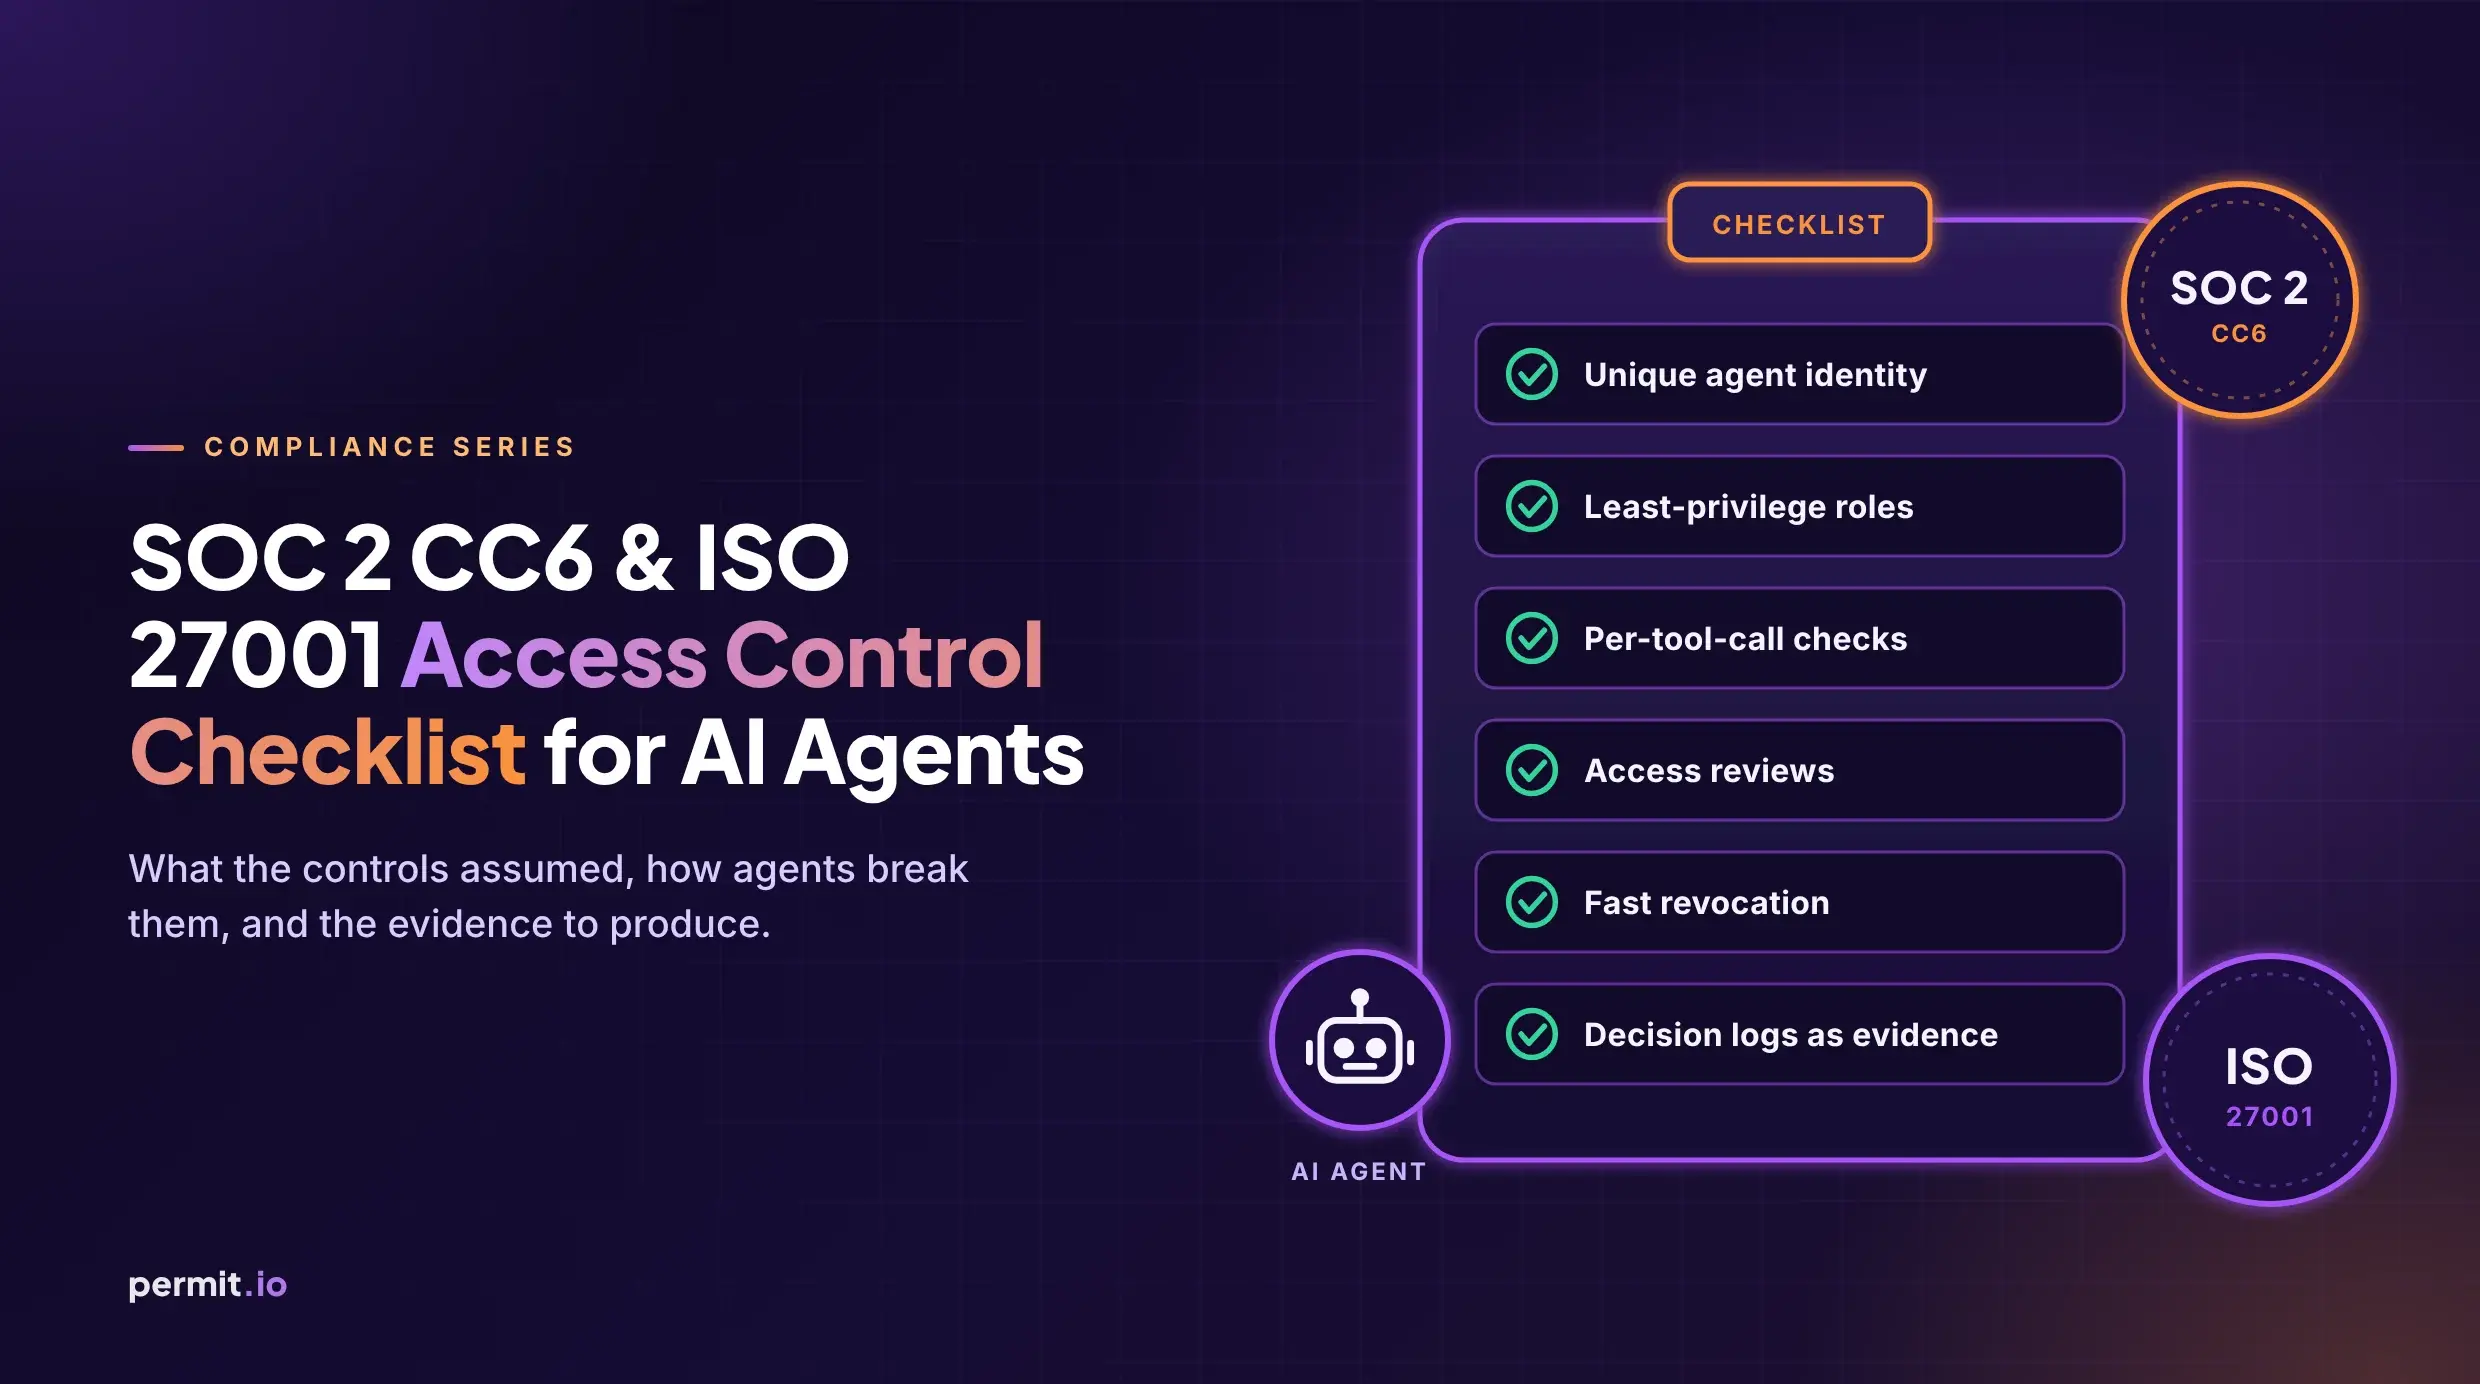
SOC 2 CC6 and ISO 27001 access control checklist for AI agents: what controls assumed, how agents break them, evidence to produce.

Or Weis
Regulators’ “prove it” maps to PEP + PDP + decision logs: enforce in the app, decide in a local PDP synced by OPAL, and keep explainable allow/deny evidence.