Decision logs
Every access decision, recorded with its reason
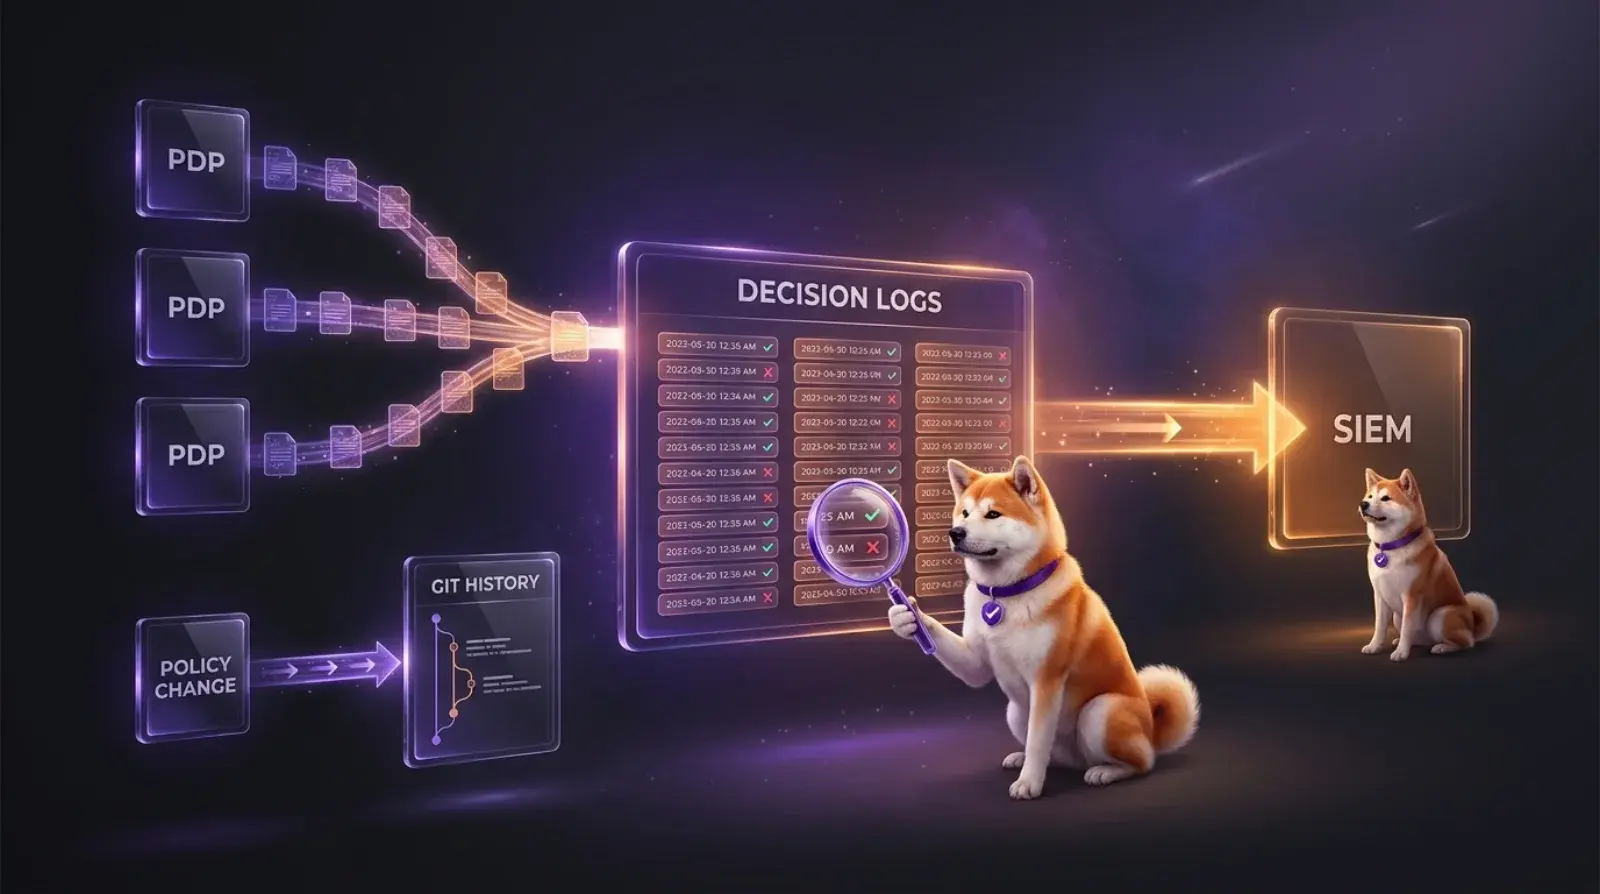
Audit logs are generated by enforcement itself. Each check already knows the user, the action, the resource, and the tenant, so the log entry exists the moment the decision is made, not when someone reconstructs it later.
- Audit logs record who did what, to which resource, and whether it was allowed.
- Decision logs go further and record why the policy engine decided the way it did.
- Filter by user, date, decision, and tenant in the dashboard, or query through the API.
- PDPs write logs to standard output for any log pipeline, and the Logs Forwarder can ship them straight to Elasticsearch.
pdp values.yaml
pdp:
  logs_forwarder:
    enabled: true
    type: elasticsearch
    elasticsearch:
      host: logs.internal.example.com
      port: 9200
      index: permit-decisions