
SCIM provisioning
Joiners, movers, and leavers, straight from the directory
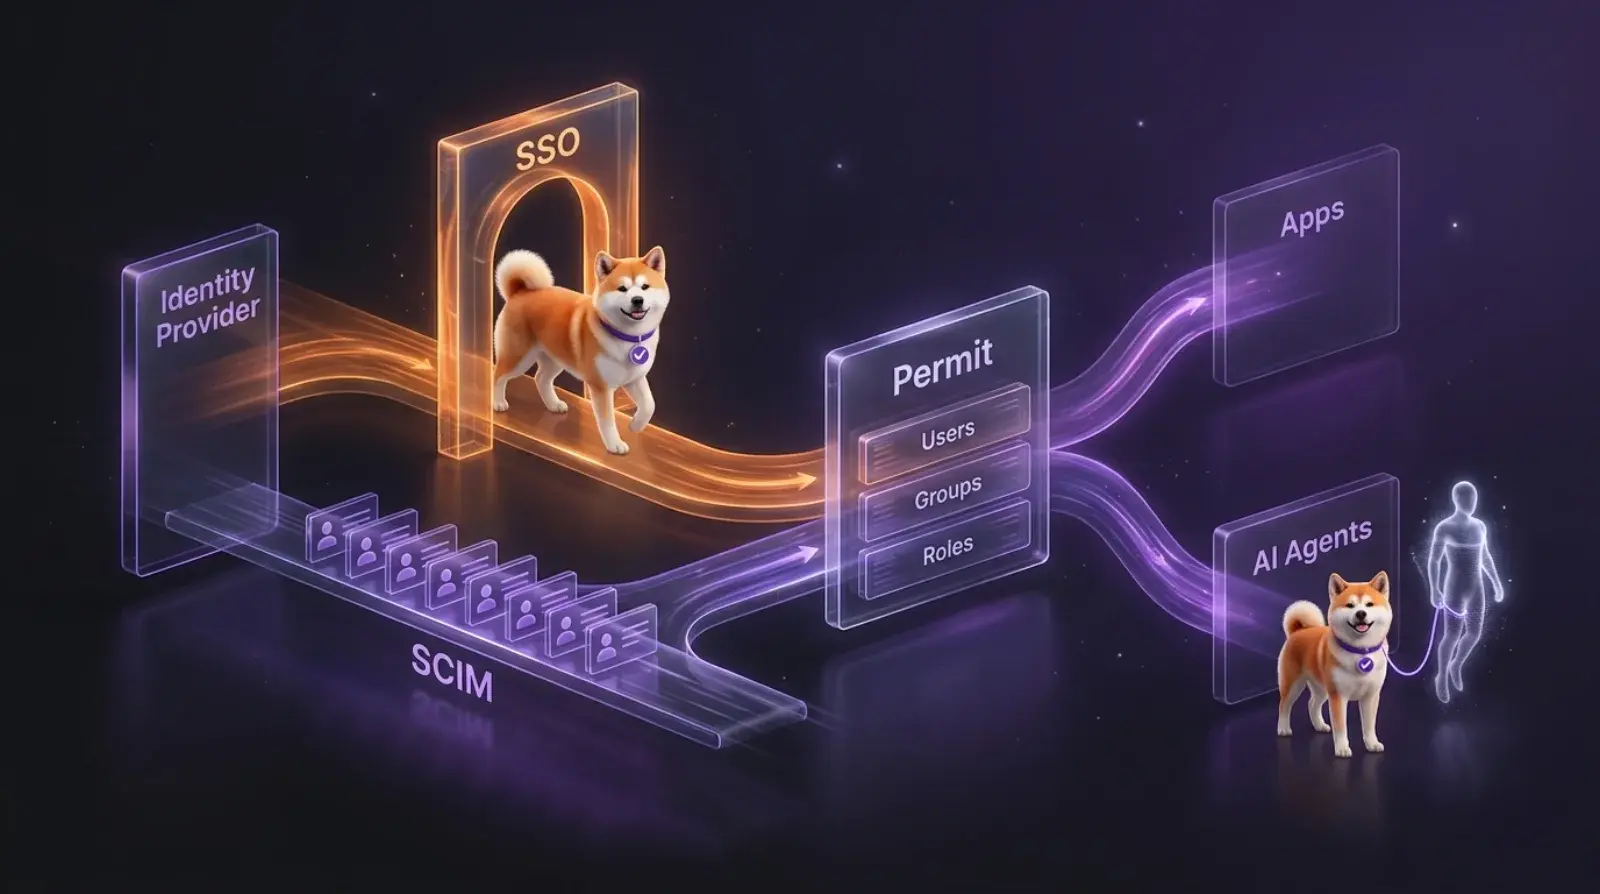
Access should change when the directory changes, not when someone next runs a sync script. Permit runs a SCIM 2.0 server, so Okta or Entra ID provision users and groups into authorization the same way they provision any other application.
- Users and groups sync over SCIM 2.0. Groups become roles, and group membership becomes a role assignment.
- Your identity provider pushes creates, updates, and deactivations, so a leaver loses access through the same connection that granted it.
- Tenant-aware endpoints let each of your enterprise customers point their own identity provider at their own tenant, with role assignments kept separate per tenant.
- Step-by-step guides for Okta and Entra ID, and a separate endpoint for the EU region.
SCIM base URLs
# One environment for all users
https://scim.permit.io/scim/v2/{project}/{environment}

# One connection per customer tenant, assignments isolated per tenant
https://scim.permit.io/scim/v2/{project}/{environment}/v2/{tenant}