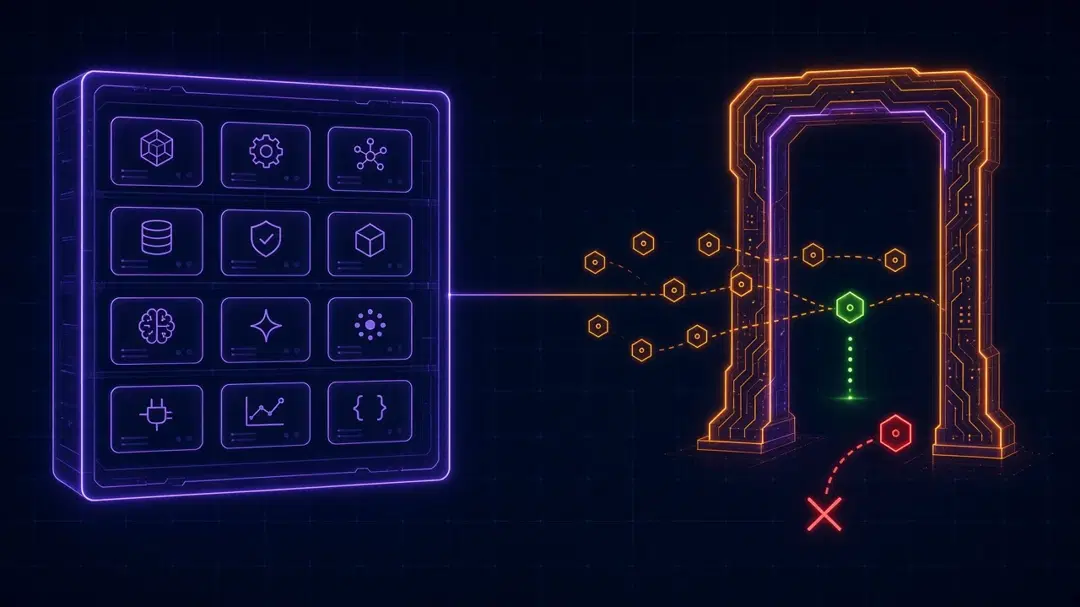
An MCP registry and an MCP gateway get mentioned in the same breath, but they answer different questions at different times. A registry answers "which MCP servers exist, who published them, and how do I install or reach them?" It is consulted before a connection is made. A gateway answers "may this user's agent call this tool, with these arguments, right now?" It sits in the path of every tool call, so the agent gets the access the user agreed to and does not simply inherit everything the user can do.
Teams that adopt one and assume it covers the other end up with a gap. This post explains what the official MCP Registry does and doesn't do, based on its own documentation, what a gateway adds at runtime, and how the two fit together.
What an MCP registry is
The official MCP Registry launched in preview in September 2025. Its documentation describes it as the official centralized metadata repository for publicly accessible MCP servers, and still labels it a preview in which breaking changes or data resets may occur before general availability.
A few properties matter for security planning:
- It stores metadata, not code. The registry is a metaregistry. Each entry is a
server.json document with the server's name, where to get it (an npm, PyPI or OCI package, or a remote URL), how to run it, and a description. The code itself lives in package registries.
- Names are tied to verified namespaces. A server named
io.github.alice/weather-server can only be published by someone who authenticated as that GitHub account, and com.example/server requires proving control of example.com through a DNS or HTTP challenge, according to the authentication guide.
- It is public only. The registry doesn't list private servers. For those, the docs recommend running your own private registry that implements the same OpenAPI spec.
- It feeds other registries. The docs say the registry is meant to be consumed mainly by downstream aggregators and subregistries, not directly by host applications. Aggregators pull from its unauthenticated read-only API and add curation, ratings or security scanning.
Here is a real lookup from the registry's API, trimmed. At the time of writing it returns the GitHub MCP server's latest entry:
curl "https://registry.modelcontextprotocol.io/v0.1/servers/io.github.github%2Fgithub-mcp-server/versions/latest"
{
  "server": {
    "name": "io.github.github/github-mcp-server",
    "version": "2.2.0",
    "packages": [
      { "registryType": "oci", "identifier": "ghcr.io/github/github-mcp-server:2.2.0", "transport": { "type": "stdio" } }
    ],
    "remotes": [
      { "type": "streamable-http", "url": "https://api.githubcopilot.com/mcp/" }
    ]
  },
  "_meta": {
    "io.modelcontextprotocol.registry/official": { "status": "active", "isLatest": true }
  }
}
That entry tells you who published the server, which version is current, and where to fetch or reach it. It tells you nothing about what a given agent should be allowed to do with it.
What a registry does not do
The registry is explicit about its limits. Its moderation policy says consumers should assume minimal-to-no moderation. It removes illegal content, malware, spam and non-functioning servers, and it does not remove low-quality servers or servers with security vulnerabilities. Security scanning is delegated to package registries and downstream aggregators. When a server is removed, its status is set to deleted while the metadata stays readable through the API, so anything that syncs from the registry should check that field.
Beyond moderation, a registry has no view of runtime at all:
- It doesn't know which human is behind a session or which agent is acting for them.
- It never sees a
tools/call request or its arguments.
- It can't stop a legitimate, verified server from being used to delete a repository or export a customer list.
- It doesn't keep a record of what any agent did.
Namespace verification proves where a server came from. It doesn't prove the server is safe, and it doesn't make any particular call appropriate.
What an MCP gateway is
An MCP gateway is a proxy between MCP clients and the MCP servers they connect to. Because every request passes through it, it can make and record a decision for each one. A gateway typically handles:
- Authentication: who the human behind the agent is, usually through your existing identity provider.
- Authorization: whether this user and this agent may call this tool on this server, checked against policy on every call.
- Consent: how much access the user agreed to give the agent.
- Audit: a log of each decision with the user, agent, tool, server, time and result.
The registry works at the level of server listings, and the gateway works at the level of individual calls. For the difference between a gateway and a plain proxy, see MCP gateway vs MCP proxy.
Side by side
|
MCP registry |
MCP gateway |
| Question it answers |
Which servers exist and who published them |
Whether this call may run now |
| When it acts |
Before connection (discovery, install) |
On every tool call |
| Unit of decision |
A server version |
A user, agent, tool and arguments |
| Identity it checks |
The publisher's namespace |
The end user and the agent |
| Security it provides |
Publisher authenticity, basic takedowns |
Per-call authorization, consent, audit |
| What it misses |
Runtime behavior, users, arguments |
Whether a server should be in your catalog at all |
Use both: catalog first, calls second
The two controls stack. A workable setup looks like this:
- Discover from the official registry or a subregistry. Use namespace verification to confirm the publisher, and check the
status field on every sync.
- Vet and approve into your own catalog. Since the official registry doesn't scan or moderate deeply, decide which servers and versions your organization allows. A private registry that implements the same spec is one way to hold that list.
- Expose approved servers only through the gateway. Clients connect to the gateway URL, not to the server directly, so there is one enforcement point.
- Authorize each call at the gateway. Bind every call to a user and an agent, and check the tool and its risk against policy.
- Keep the audit trail at the gateway. It is the enforcement point that sees and records every decision.
Some products combine both roles in one MCP gateway registry, so the registration step also decides where the gateway sends traffic. AWS's Security Bulletin 2026-180-AWS shows the risk: in mcp-gateway-registry versions 1.0.3 through 1.34.0, a user allowed to register or edit a server could point its upstream address at internal services (CVE-2026-125926, fixed in 1.35.0). Treat registering and editing servers as a privileged permission, limit the gateway's outbound traffic, and review stored upstream addresses and logs after upgrading. We walk through it in MCP gateway security.
Supply chain and runtime are linked: a verified server can still be misused by a prompt-injected agent. We cover that link in the MCP server supply chain is a runtime supply chain.
Where Permit MCP Gateway fits
Permit MCP Gateway, which is generally available, is the runtime half of this picture. As shared in our MCP Gateway docs, it is a proxy between MCP clients such as Cursor, Claude Desktop, Claude Code and VS Code and the MCP servers they connect to. For each tool call it authenticates the human behind the agent, checks the call against policy in Permit, confirms the human consented to the agent's access level, and logs the decision. It classifies each tool by risk (read, write or destructive), denies by default until an admin grants access, and works with existing MCP servers without changing their code. You point the client at the gateway URL instead of the server URL.
Permit MCP Gateway is not a registry and doesn't replace one. Use a registry for discovery and publisher trust, and the gateway for per-call decisions.
If you want to try it, the MCP Gateway Free plan, labeled Community on the MCP Gateway pricing page, includes 10 tenants, 1 environment, 7 days of audit logs and up to 1,000 MAU across human and agentic identities.
FAQ
What is the difference between an MCP registry and an MCP gateway?
A registry lists MCP servers and verifies who published them. A gateway sits between clients and servers and decides whether each tool call may run, for which user and agent, and logs the result.
Does the official MCP Registry scan servers for security issues?
No. Its documentation says security scanning is delegated to package registries and downstream aggregators, and its moderation policy says it doesn't remove servers with security vulnerabilities.
Can I use the official MCP Registry for internal servers?
No. It lists only publicly accessible servers. Its docs recommend running your own private registry that implements the same OpenAPI spec.
Do I need a gateway if I only use verified servers?
Verification tells you who published a server. It doesn't control what an agent does with it. Per-call authorization, consent and audit happen at runtime, which is the gateway's job.
To put per-call authorization, consent and audit in front of the MCP servers you already use, try Permit MCP Gateway.