
Or Weis
Announcing Permit MCP Gateway
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Read more
Featured Stories
Or Weis
Announcing Permit MCP Gateway, a new trust and enforcement layer for MCP that brings identity, consent, fine-grained authorization, auditability, and runtime control to AI agent actions.
Gabriel L. Manor
The new Permit.io CLI brings developer-first workflows to access control. Define, test, deploy, and enforce fine-grained authorization using AI, CI/CD, GitOps, and OpenAPI — all from your terminal
Ze'ev Manilovich
Auth0 FGA provides managed relationship-based authorization built on OpenFGA. A comparison with Permit.io covering policy languages, deployment models, and enterprise features.

Or Weis
OPA vs OpenFGA vs Cedar: comparing policy engines for fine-grained authorization. Strengths, trade-offs, and use cases of OPA, OpenFGA, and Cedar for scalable access control.
Or Weis
OpenFGA alternatives for fine-grained authorization including SpiceDB, Cerbos, OPA, Cedar, and Permit.io. A comparison of relationship-based and policy-based approaches to help you choose.
Ze'ev Manilovich
WorkOS FGA extends RBAC with hierarchical resource scoping. A comparison with Permit.io covering policy languages, deployment models, and when each fits your authorization requirements.
Or Weis
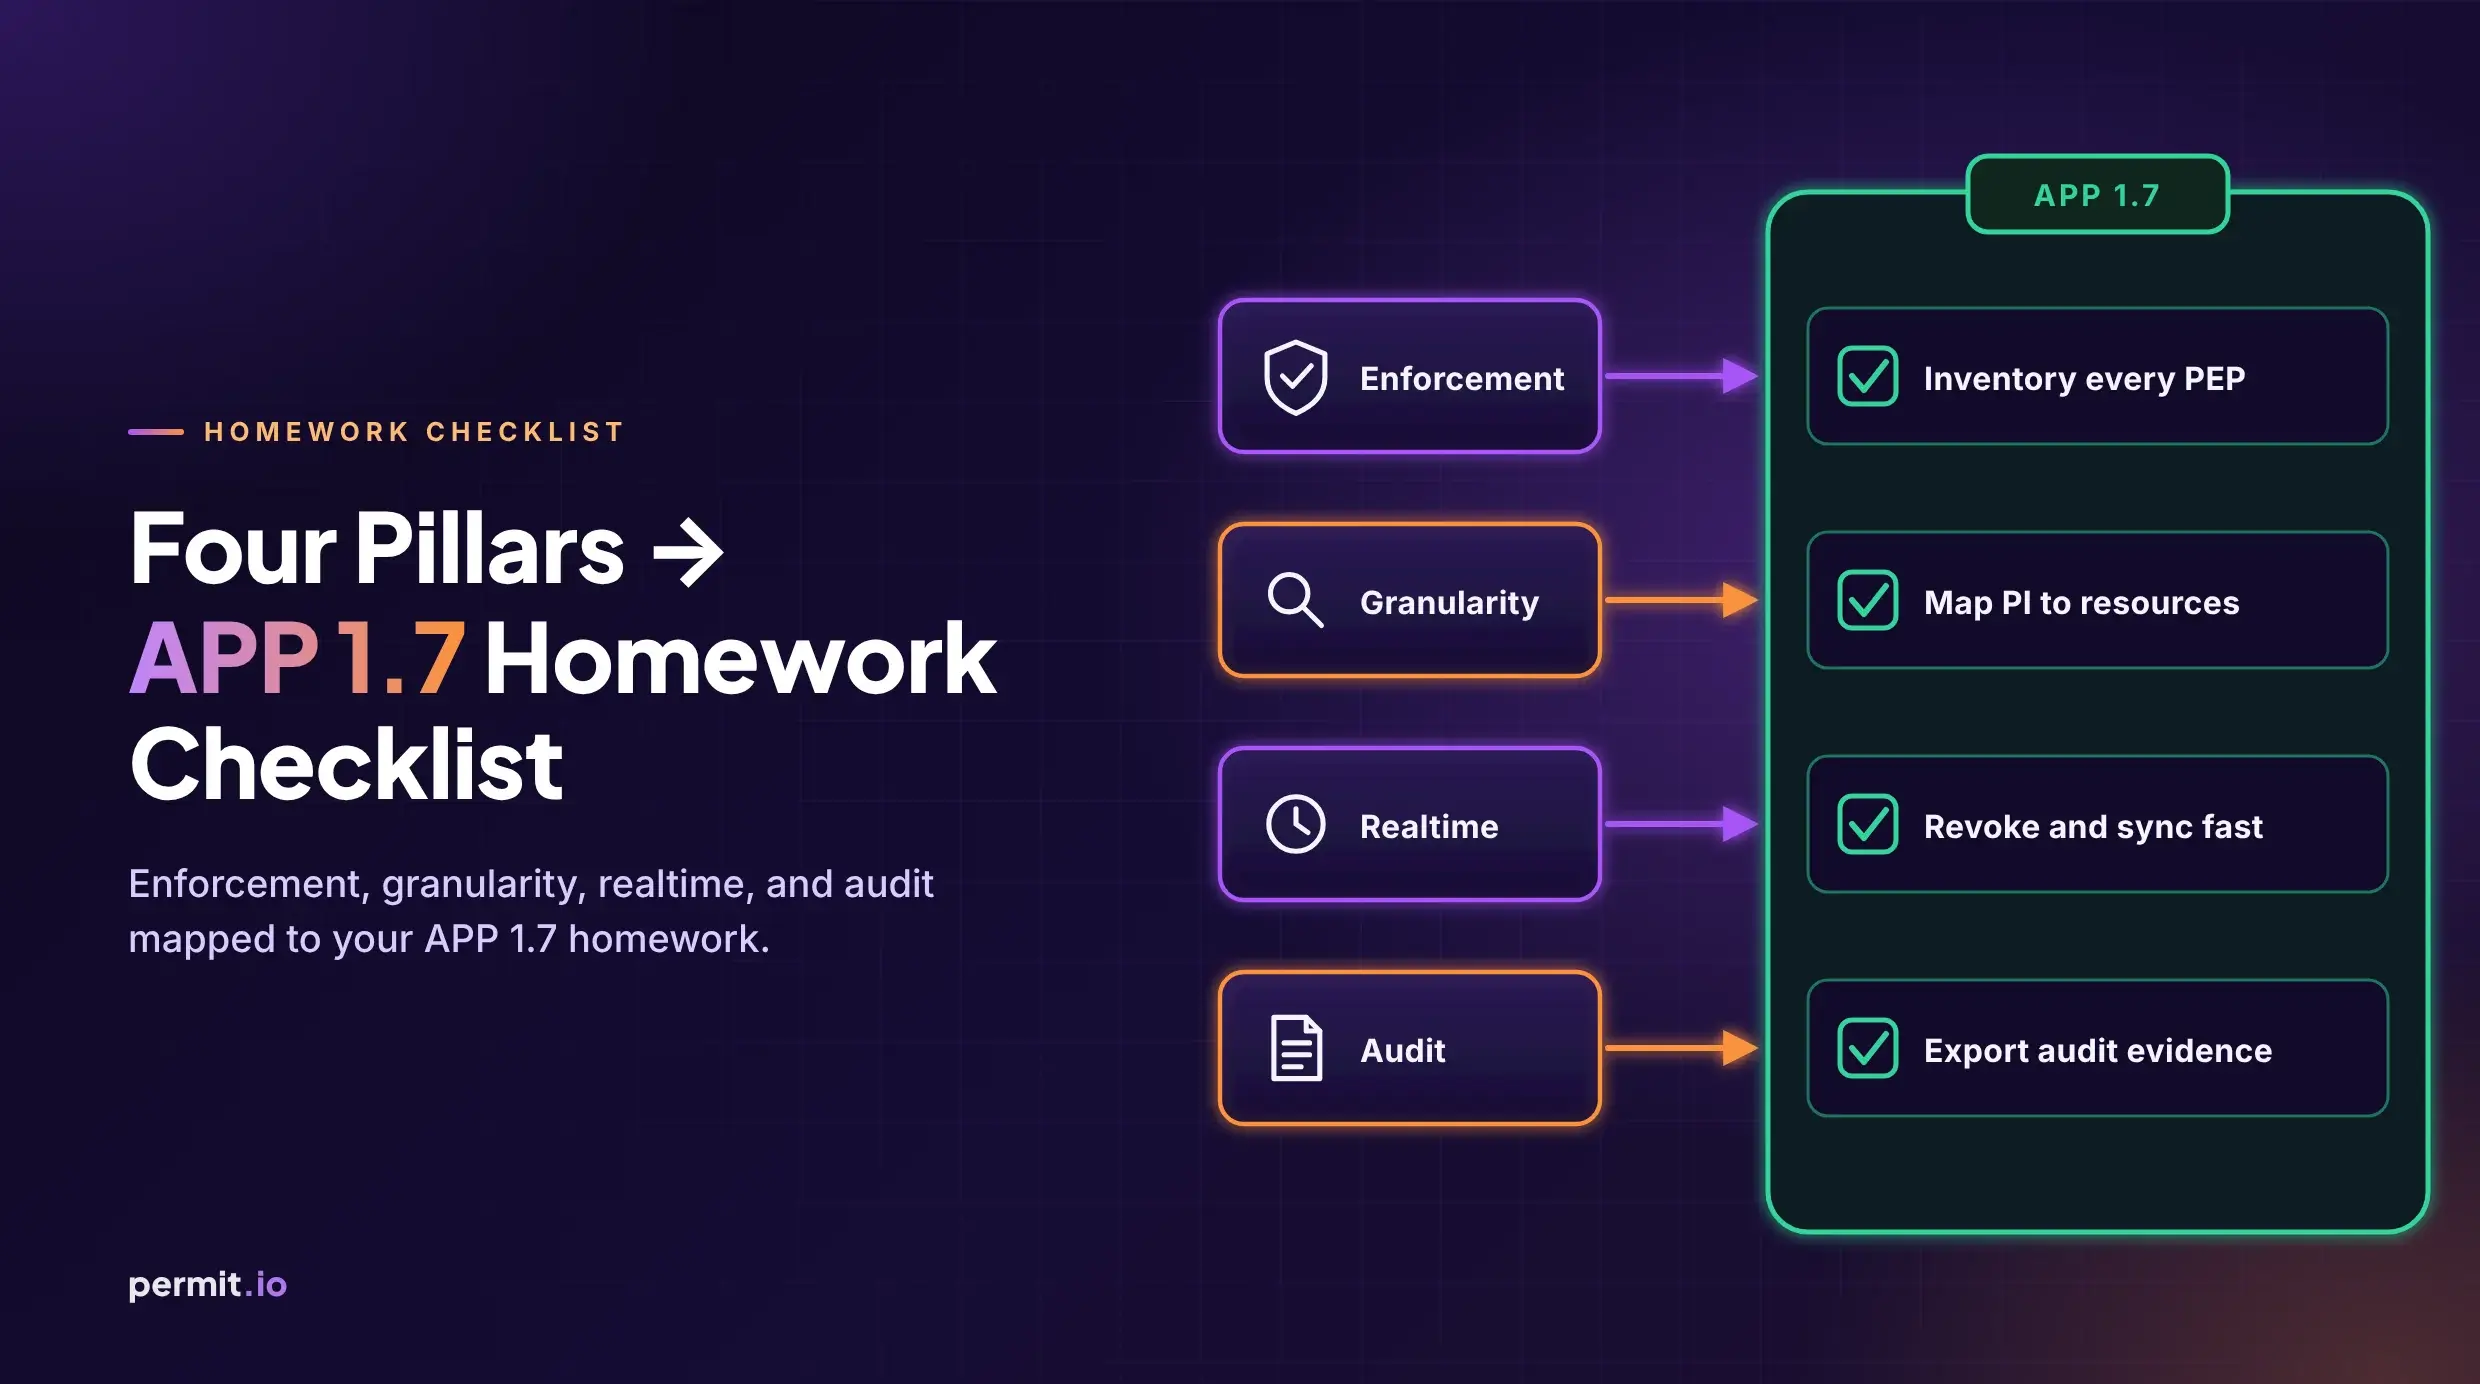
Map enforcement, granularity, realtime, and audit to APP 1.7 homework: inventory PEPs, PI→resource maps, revoke/sync, and audit/export for privacy-policy statements.
Or Weis
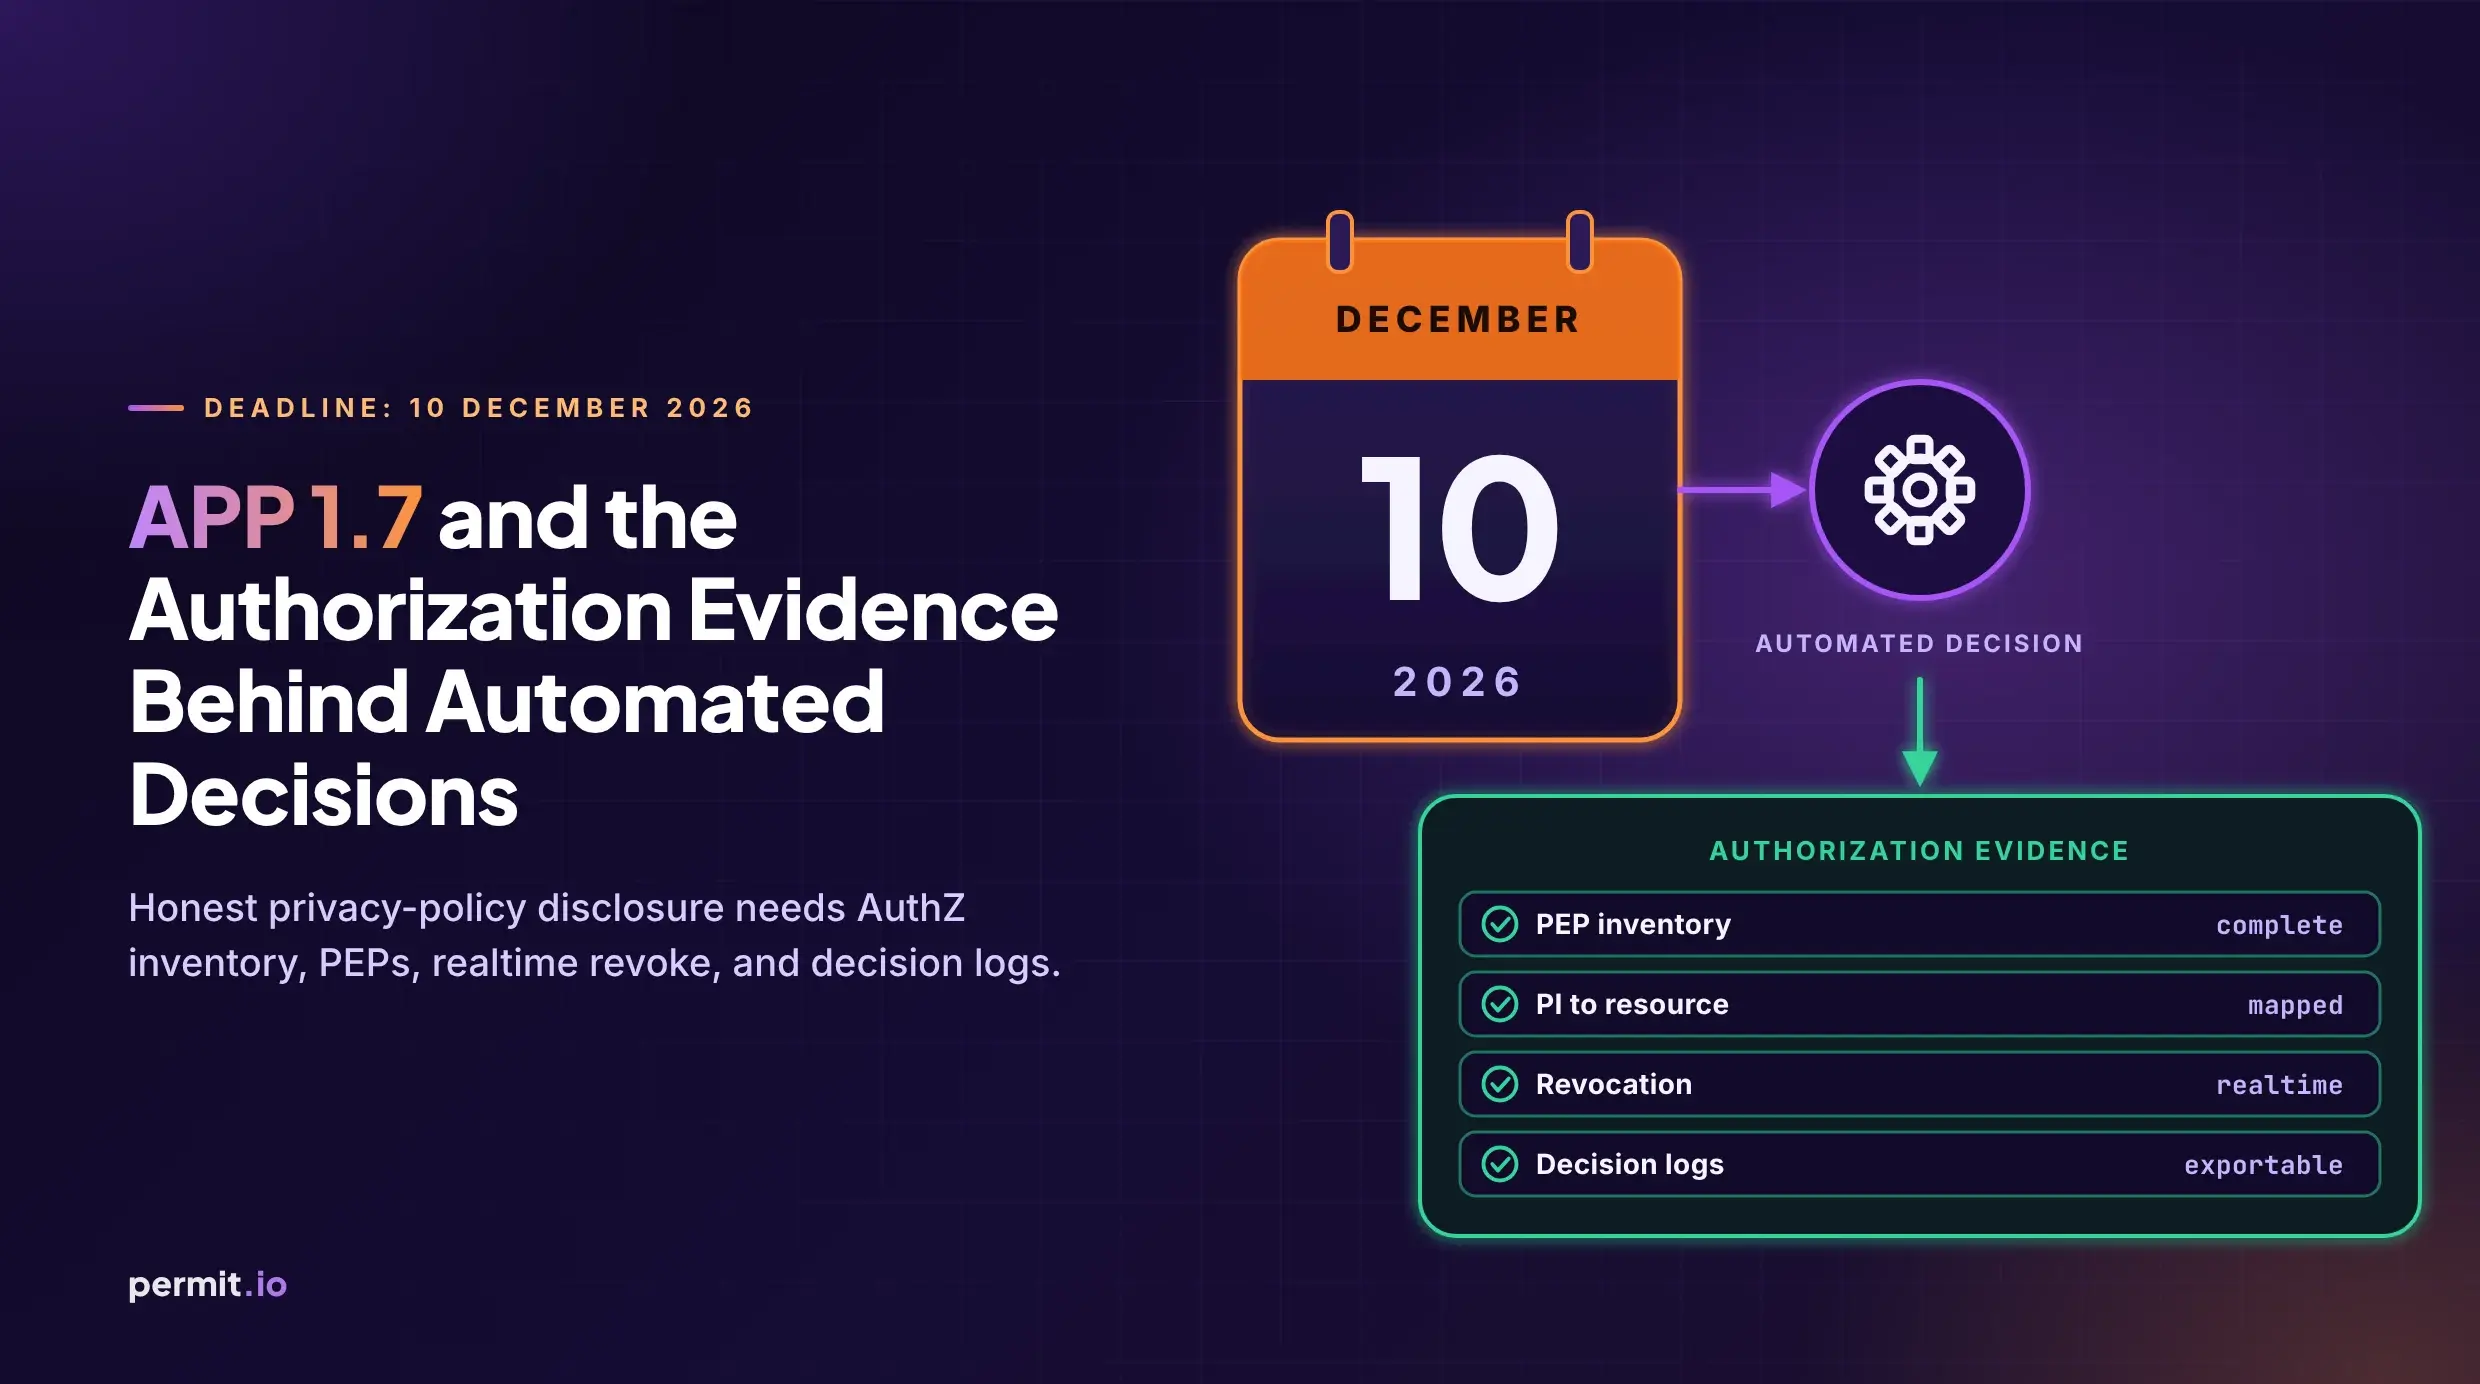
APP 1.7-1.9 commence 10 December 2026. Honest ADM privacy-policy disclosure needs AuthZ inventory, PI→resource maps, PEPs, realtime revoke, and decision-log evidence, plus a soft APRA parallel.
Ze'ev Manilovich
EN 18286:2026 is Europe's first harmonised standard under the EU AI Act. It turns Article 17's QMS requirements into auditable processes. Here's what it means for teams shipping AI agents.
Or Weis
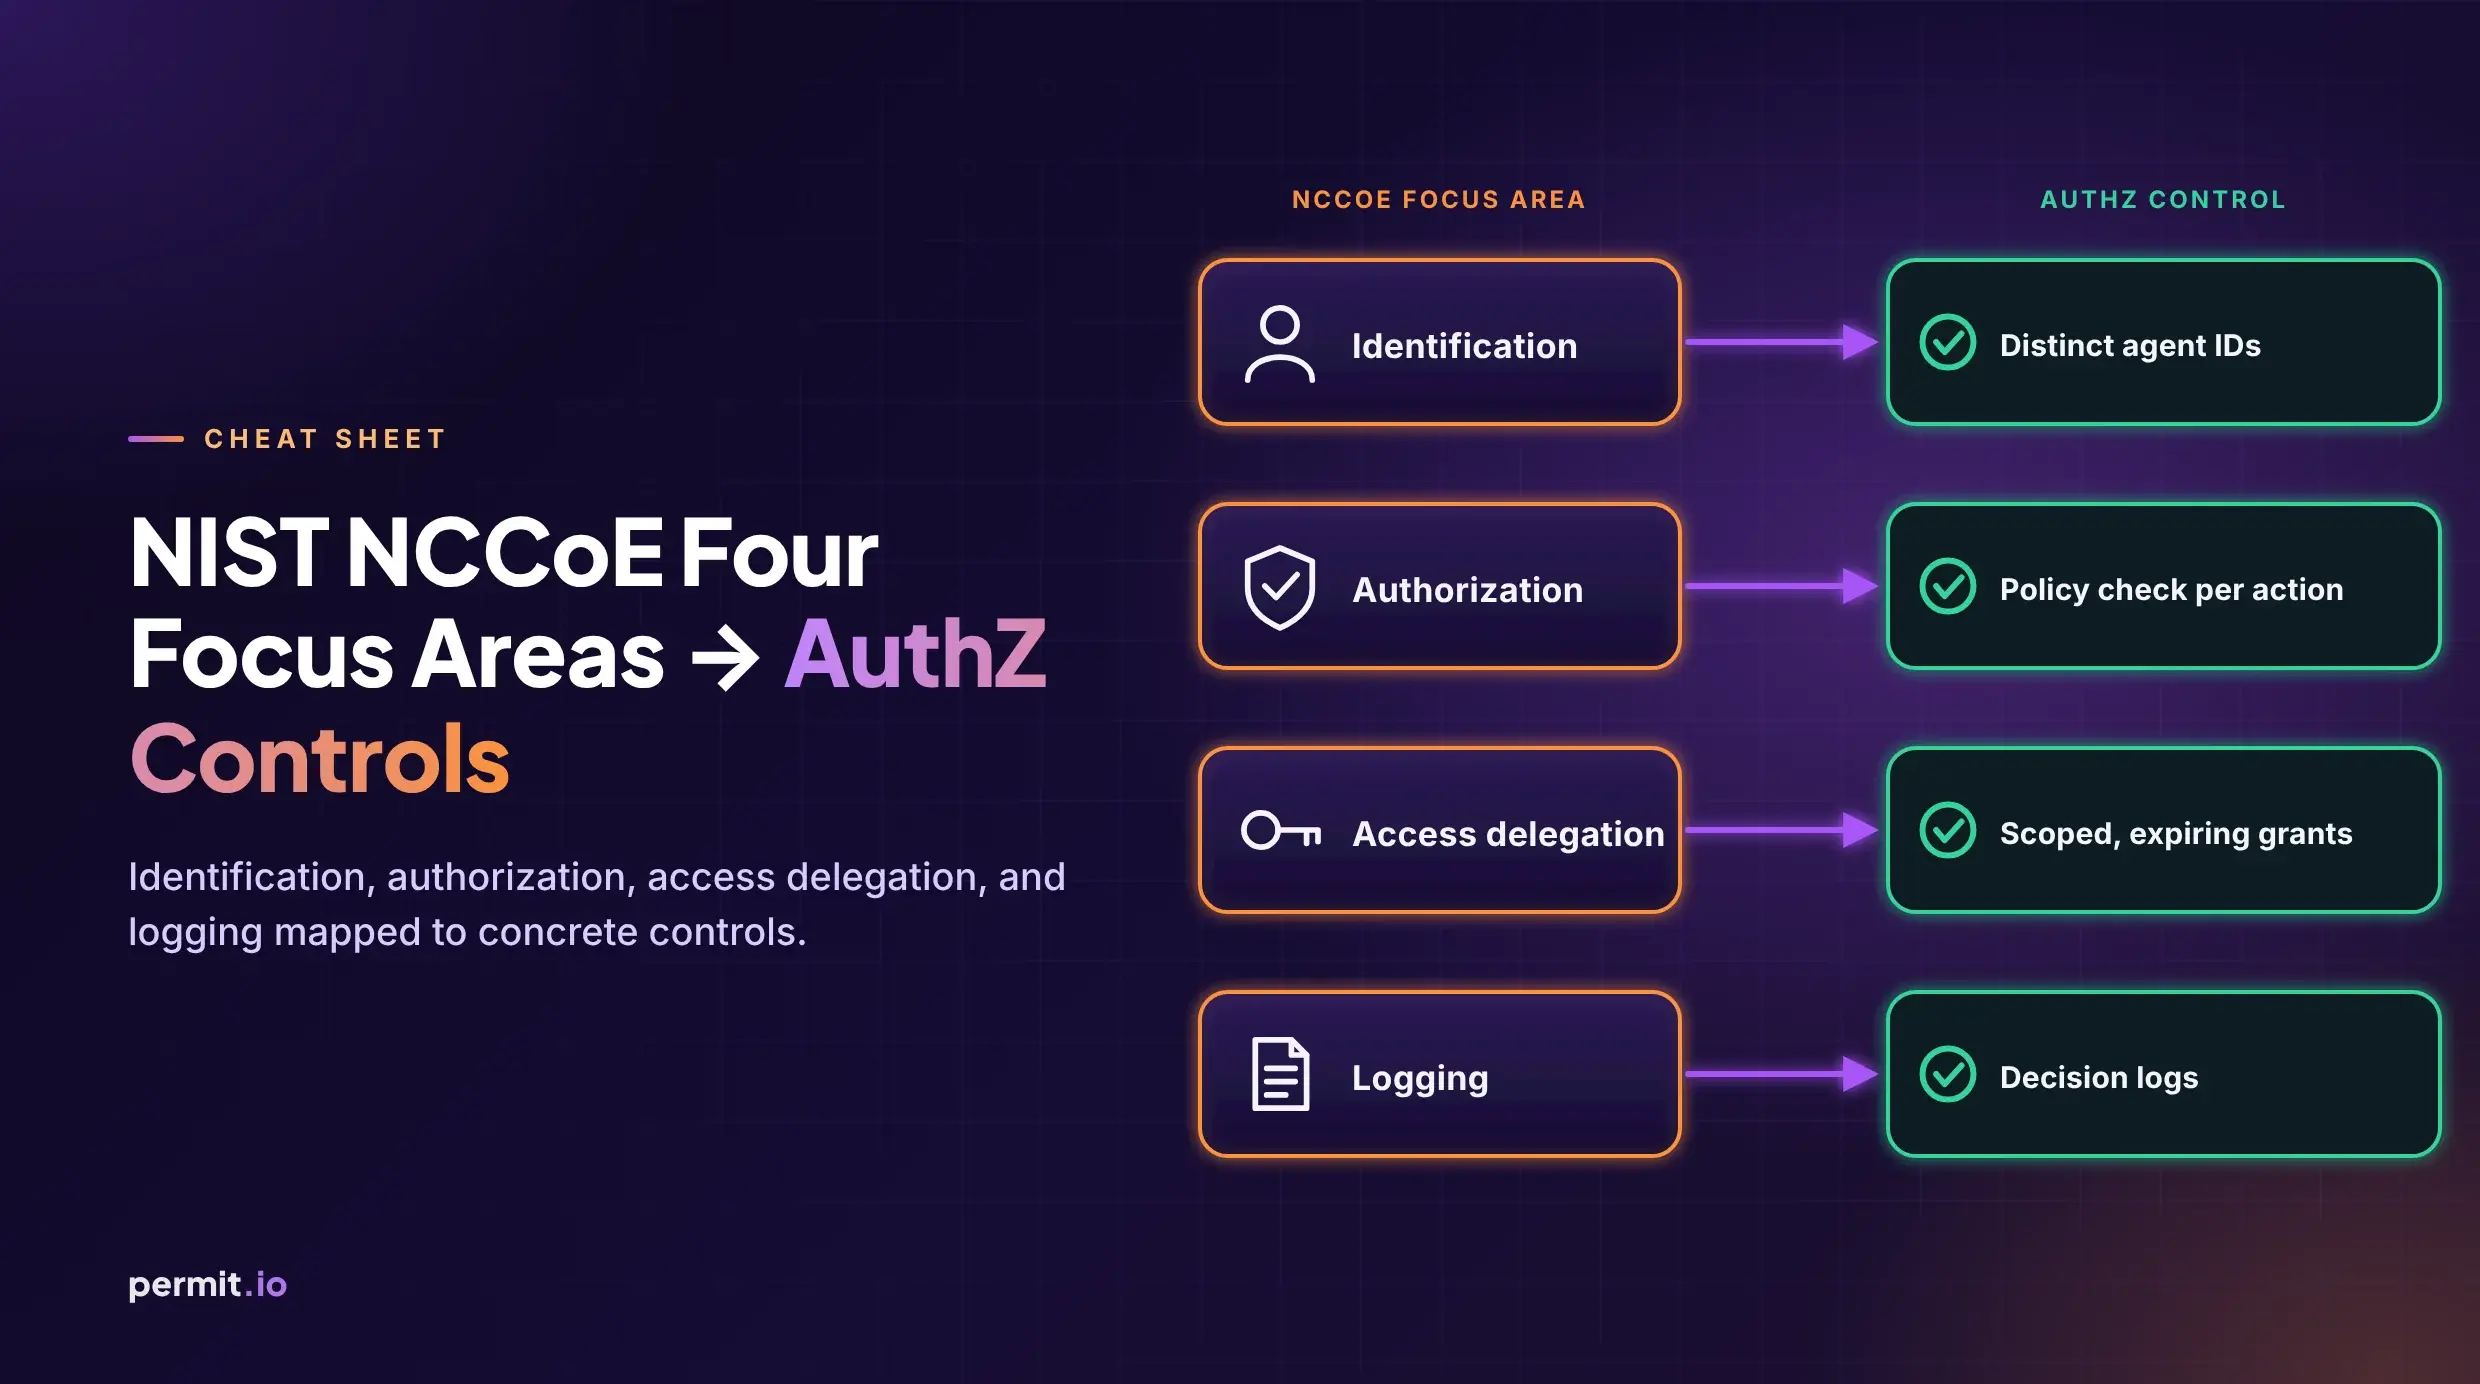
Cheat-sheet: NIST NCCoE's four focus areas (identification, authorization, access delegation, and logging) mapped to concrete AuthZ controls. Soft alignment aid, not a certification checklist.
Or Weis
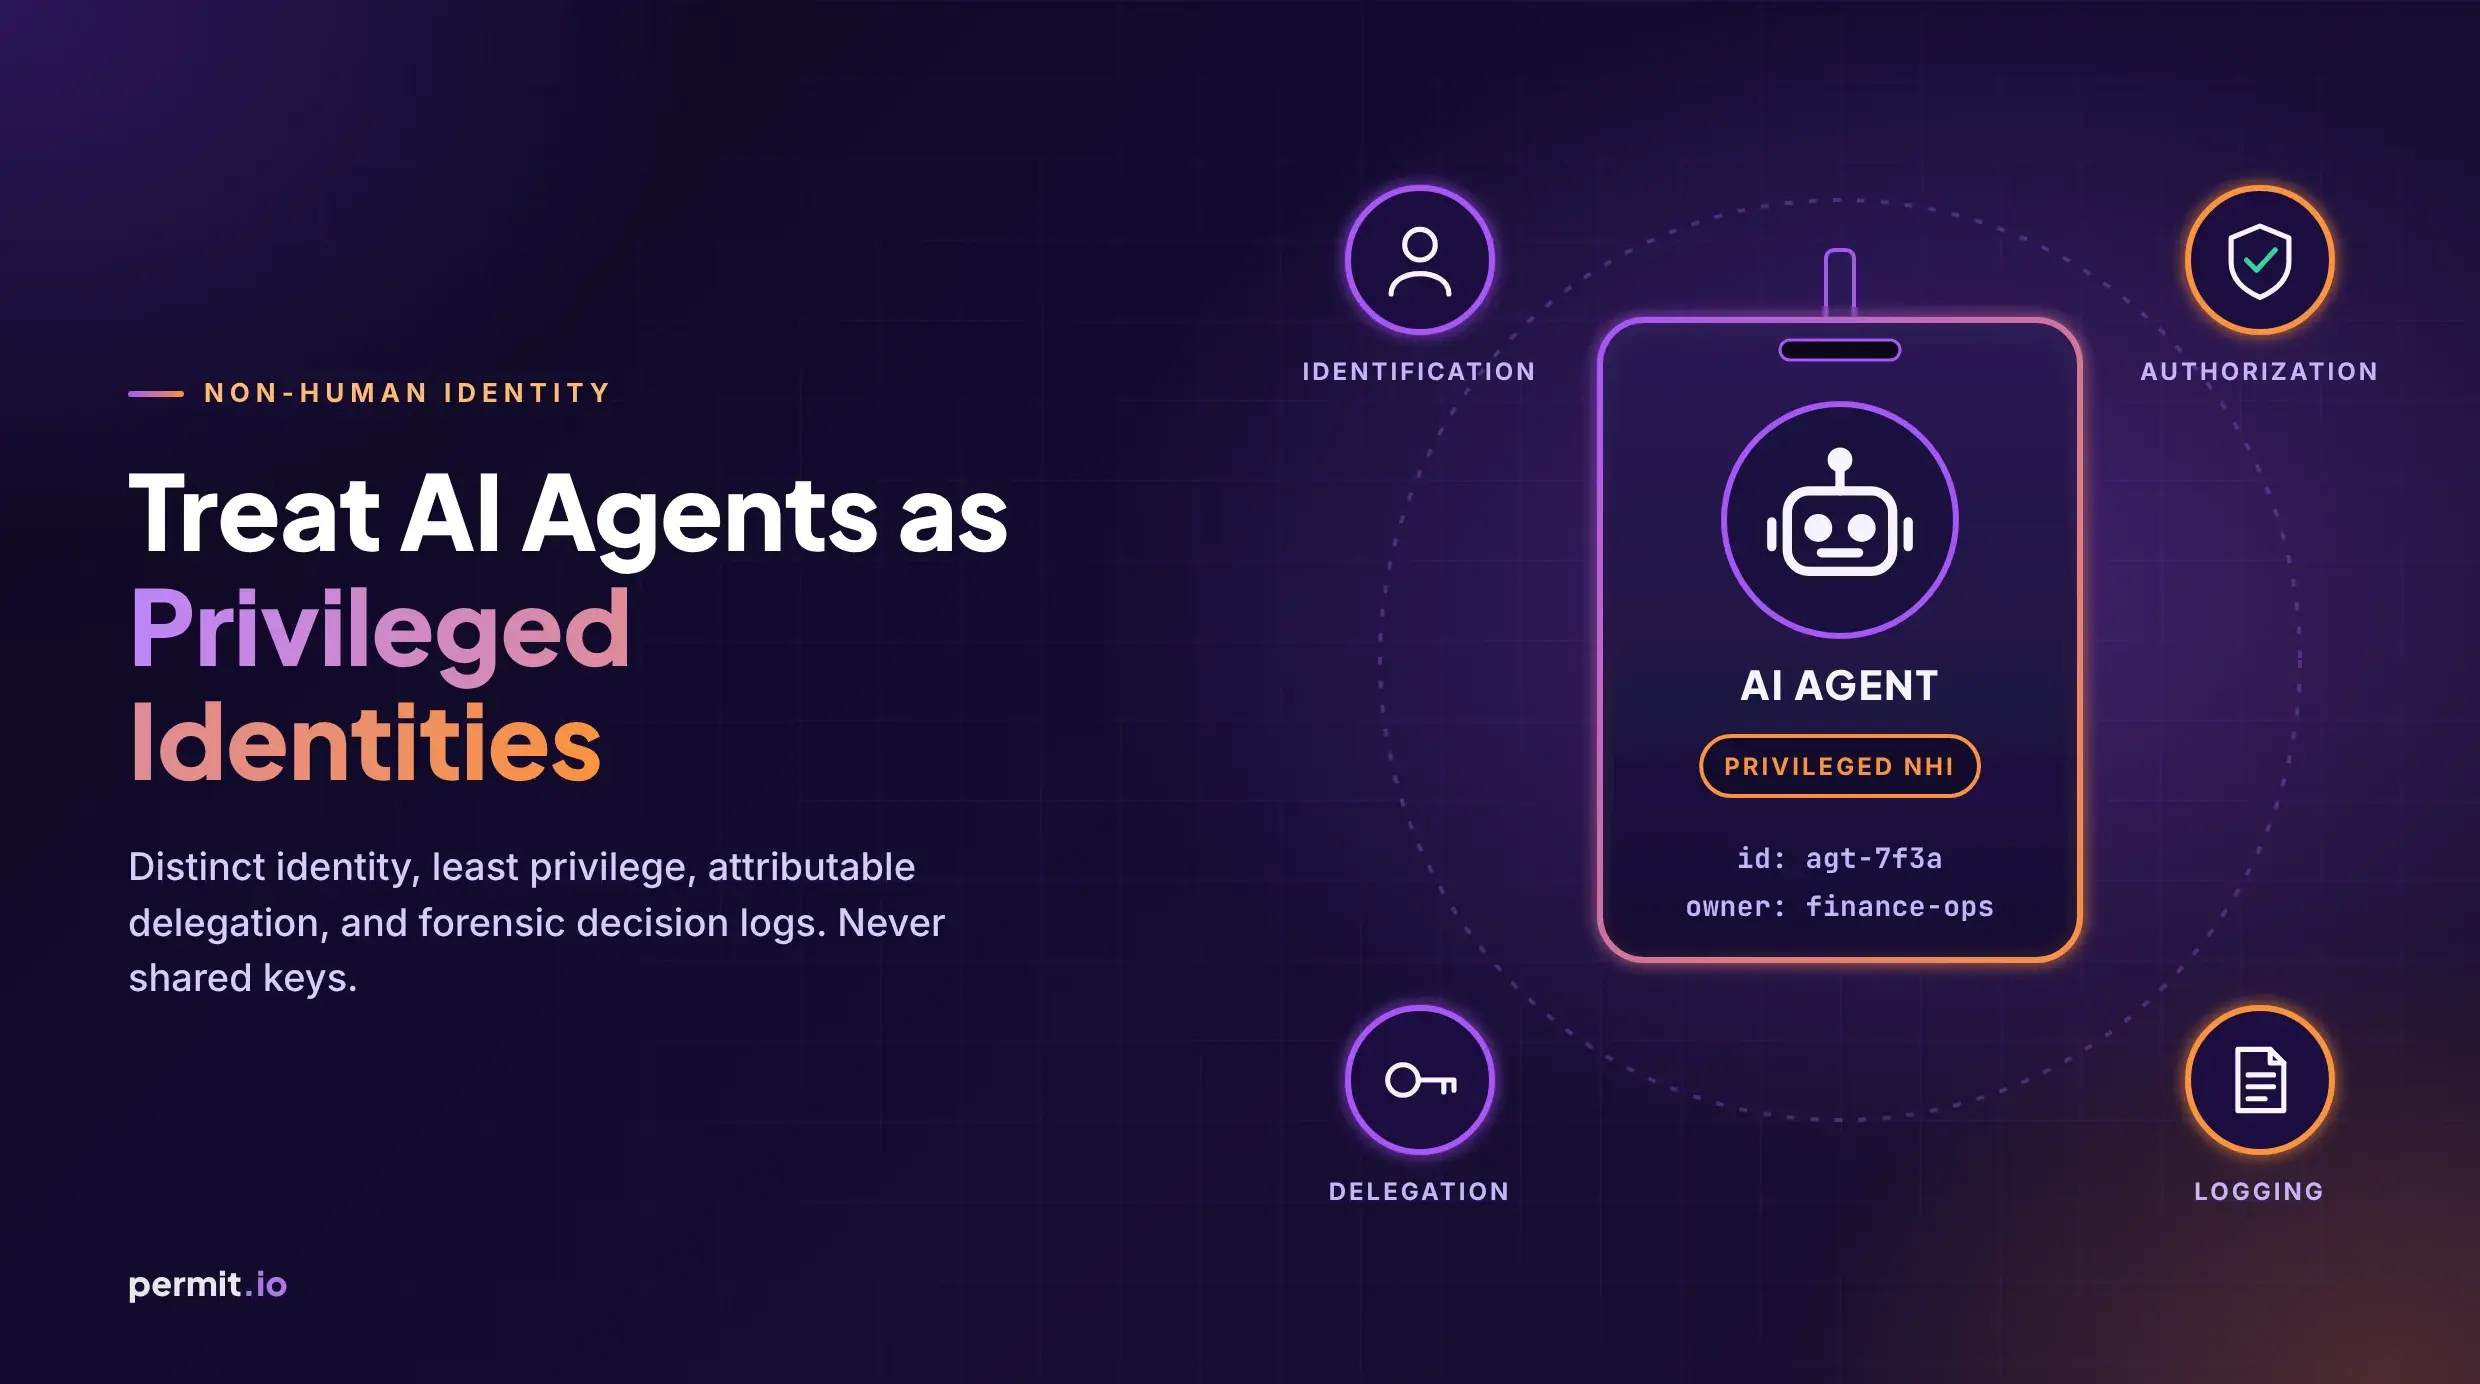
Treat AI agents as privileged NHIs: distinct identity, least privilege, attributable delegation, and forensic decision logs, not shared keys. Map to NIST NCCoE's identification · authorization · delegation · logging.
Or Weis
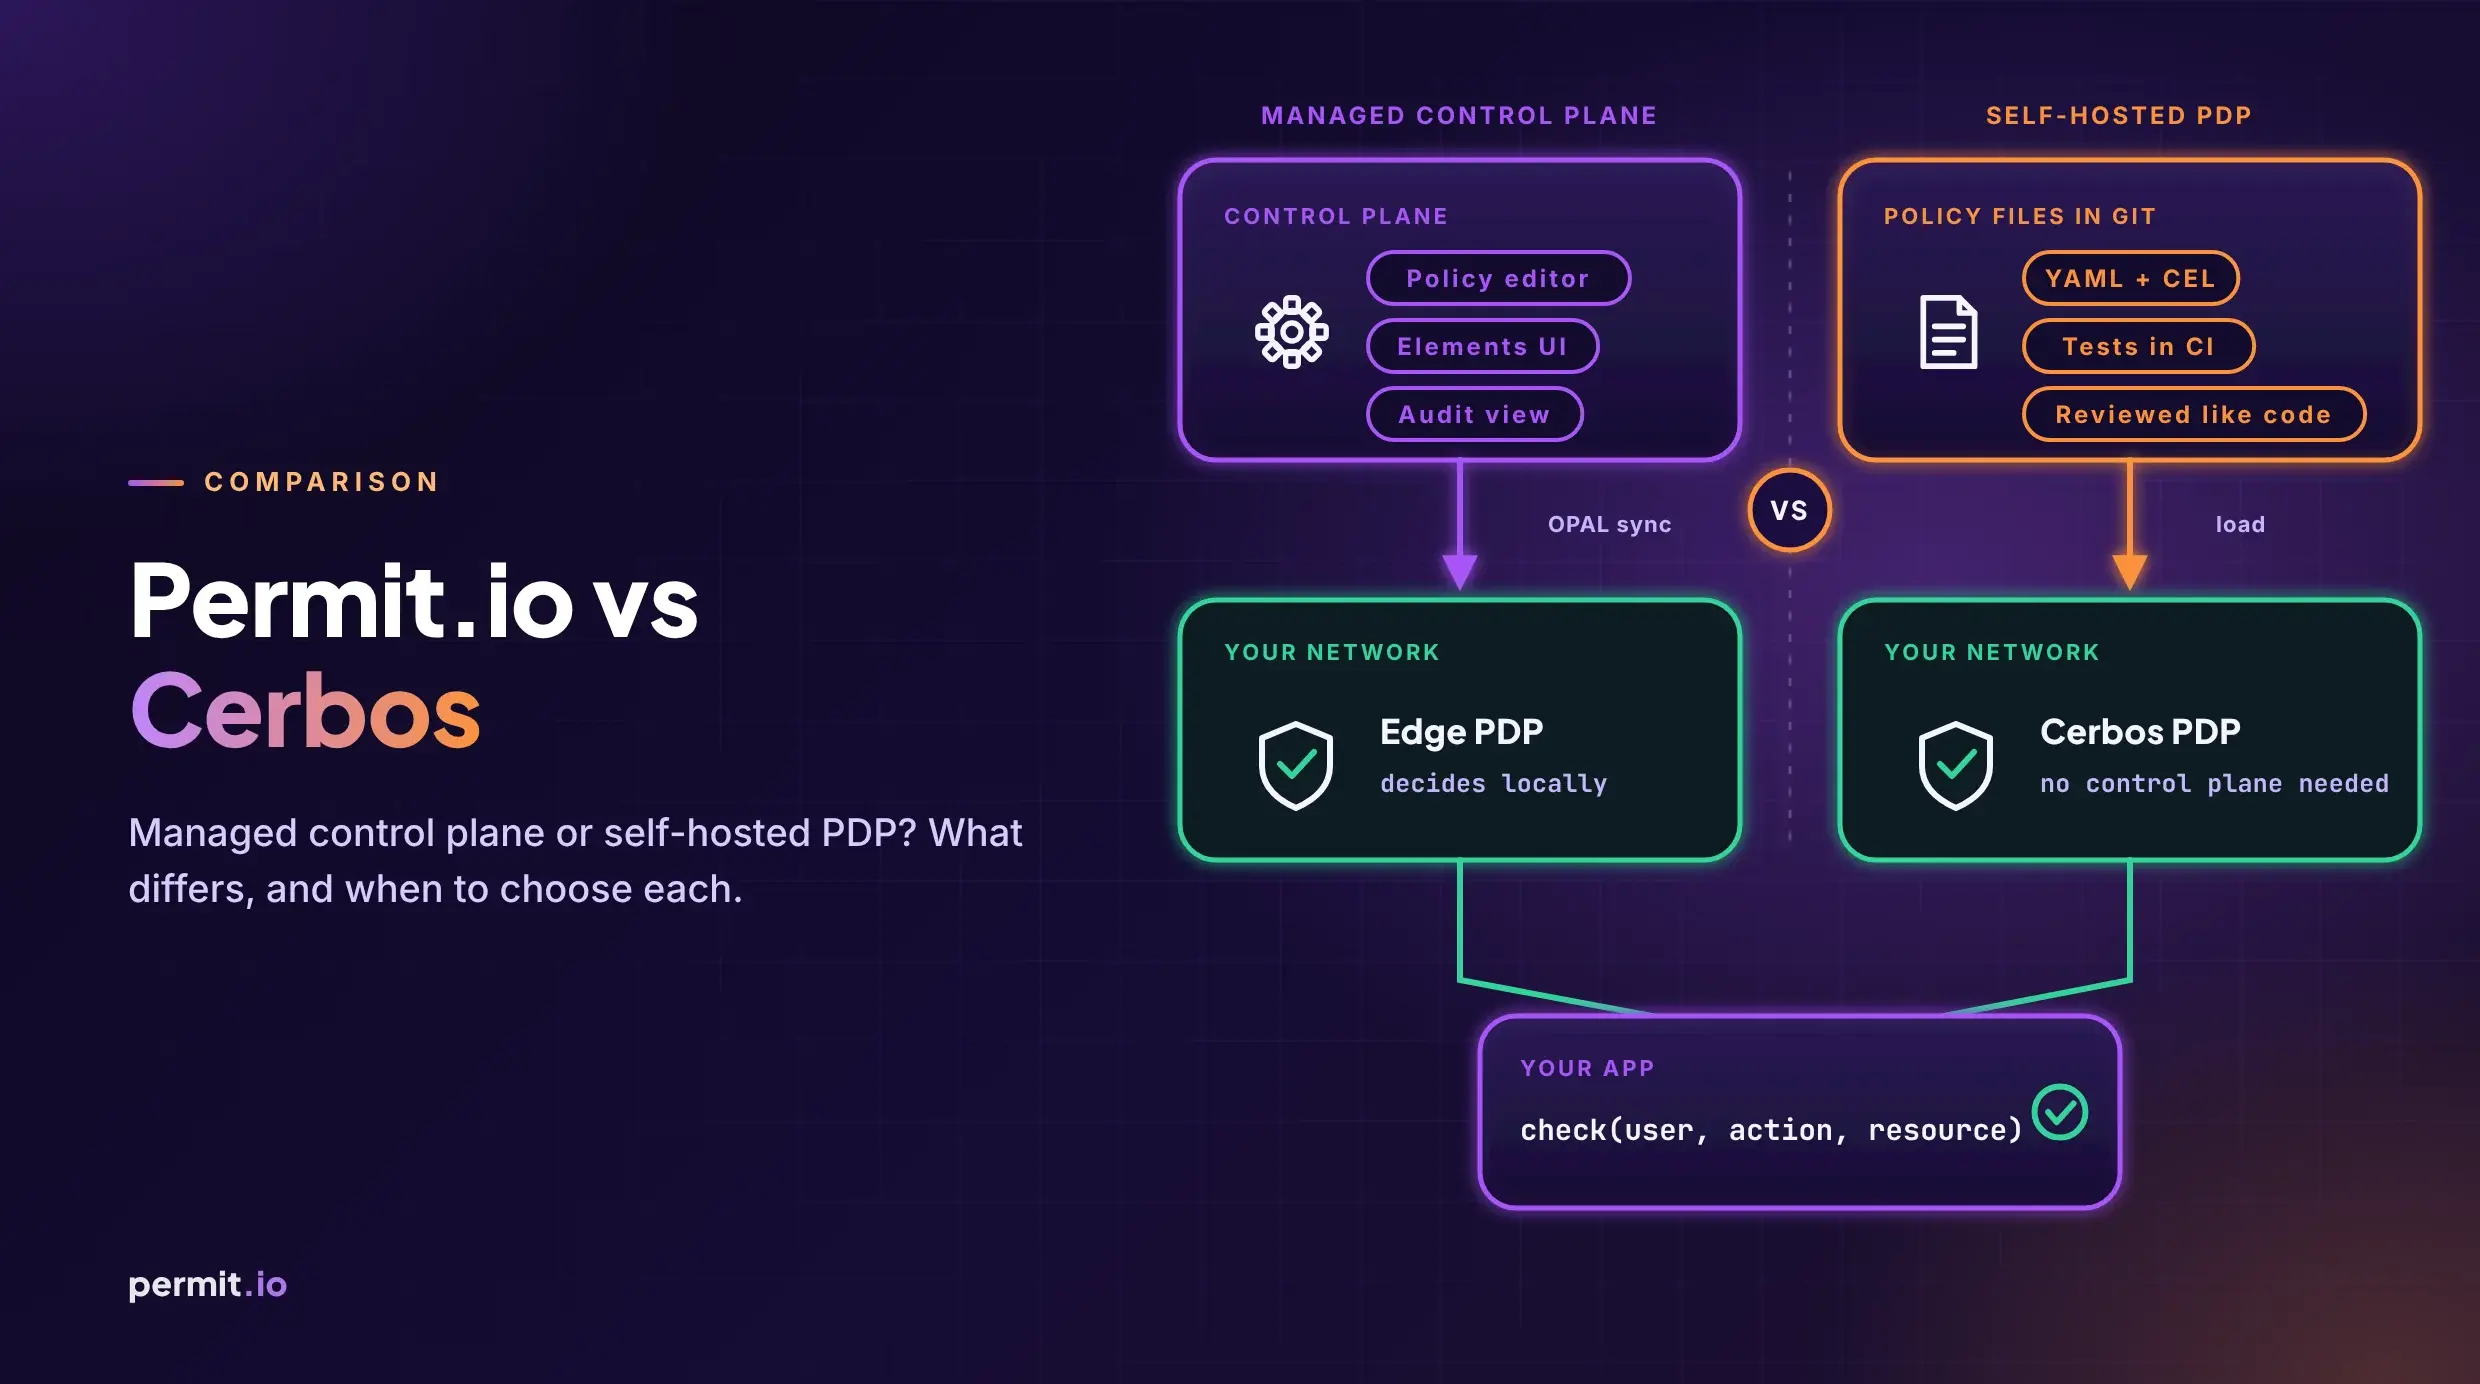
Permit.io vs Cerbos, plus Cerbos alternatives: both run an open source policy decision point next to your app. Managed control plane vs self-hosted PDP, with a table and when to choose each.
Or Weis
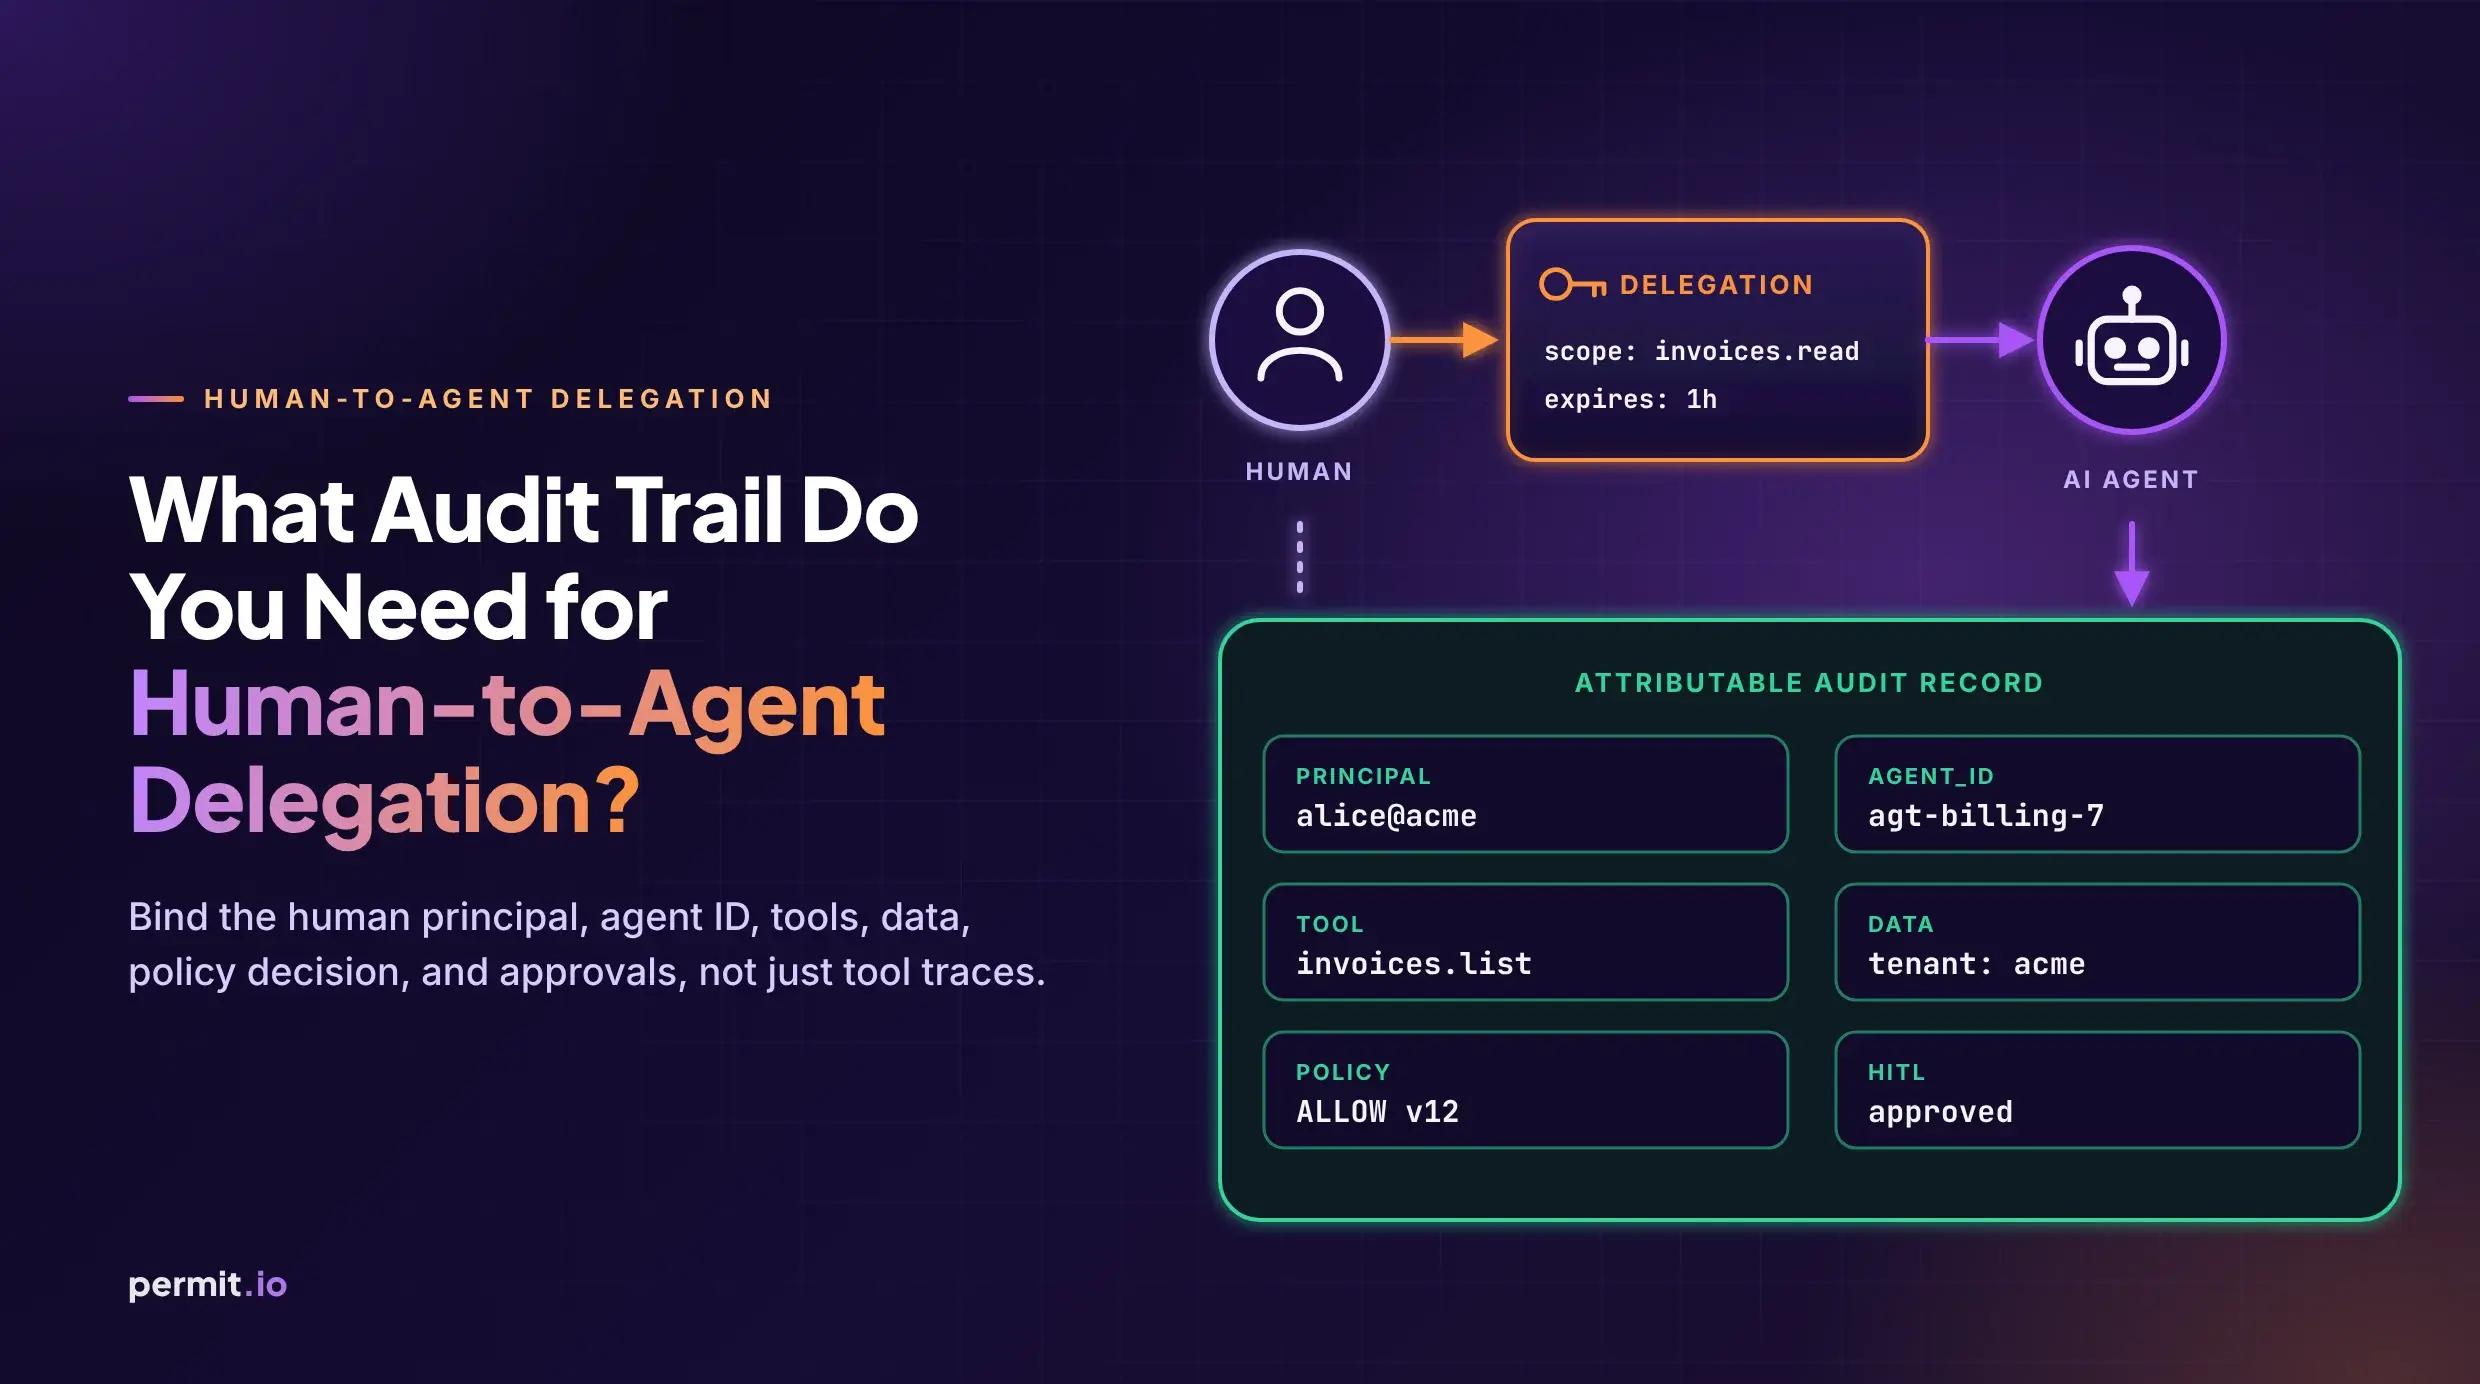
For human-to-agent delegation, bind human principal, agent ID, tools, data, policy decision, and HITL, not just tool traces, into an attributable audit trail.
Ze'ev Manilovich
Oso Cloud acquired by Tiny (announced Oct 6, 2026), most of the team joined Temporal. A practical guide to Oso alternatives, mapping Polar to RBAC, ReBAC and ABAC, and migration planning.